Category: BLOG

  • Software Spend Control for Remote Teams: Stop Surprise Bills

    Software Spend Control for Remote Teams: Stop Surprise Bills

    Example scenario: a twelve-person remote team closes its books and finds a $640 annual renewal for a design tool nobody has opened since spring. The person who signed up left four months ago. The charge landed on the founder’s card along with forty other software payments, so nobody noticed the renewal reminder, and the vendor’s refund window has already closed.

    Surprise software charges are rarely about one bad purchase. They come from a missing system: no clear owner per tool, no regular review, and one card that pays for everything. Remote teams feel this more than office teams because people sign up for tools on their own, in different time zones, and nobody walks past a colleague’s desk to ask “do we still use this?”

    This guide sets out a simple software spend control system you can run in a spreadsheet and about an hour a month. It covers ownership, a review cadence, templates you can copy, and how separate prepaid cards per tool group can act as a hard ceiling.

    Why remote teams get surprise software charges

    Anyone can sign up

    Most SaaS tools take a card and start a trial in two minutes. On a distributed team, that is useful for speed and bad for visibility. Tools pile up quietly, and the person paying often has no idea who requested them.

    Seats outlive the people

    When someone leaves, their account access is usually removed, but the paid seat may stay on the invoice. Unless offboarding includes a software step, you keep paying for licenses nobody uses.

    Annual renewals are easy to miss

    Monthly charges are visible because they repeat. Annual renewals appear once, often for a larger amount, and the reminder email goes to whoever created the account.

    One card hides everything

    When every tool bills the same card, the statement becomes a long list of vendor names. Spotting the one charge that should not be there takes real effort, so it usually does not happen.

    The system: four parts

    You do not need a spend management platform to fix this. You need four habits that reinforce each other.

    1. A software register. One shared spreadsheet listing every paid tool.
    2. A named owner per tool. One person who decides whether the tool stays, and who receives its billing emails.
    3. A review cadence. A short monthly check and a deeper quarterly review.
    4. Separate payment per tool group. So a problem or an overrun in one group stays visible and contained.

    Template: the software register

    Create a spreadsheet with these columns. Fill it once from your last three months of card statements, then keep it current.

    ColumnWhat to recordWhy it matters
    Tool nameVendor and plan nameMatches the name on the statement
    Tool groupDesign, engineering, sales, AI tools, adminMaps the tool to a budget and a card
    OwnerOne person, not a teamSomeone must decide to keep or cancel
    Billing cycleMonthly or annualAnnual renewals need earlier warnings
    Next renewal dateExact dateDrives the review calendar
    Cost per cycleAmount and currencyShows what each tool costs
    Seats paid / seats usedTwo numbersExposes idle licenses
    Payment cardLast four digitsLinks charges to the register
    Billing emailShared inbox or ownerReminders reach someone who can act
    StatusActive, review, cancel by dateTurns the register into a to-do list

    Review cadence

    Monthly check (20 to 30 minutes)

    • Match each card charge to a row in the register. Any charge without a row is either a new tool or a mistake.
    • Flag renewals due in the next 45 days and send them to their owners.
    • Update seats used for tools billed per seat.
    • Check each tool group’s spend against its budget.

    Quarterly review (about an hour)

    • Ask every owner one question per tool: keep, downgrade or cancel?
    • Look for overlap, such as two video tools or three note apps.
    • Confirm billing emails still reach a current team member.
    • Reset the budget for each tool group for the next quarter.

    Offboarding step (every departure)

    • List the tools the person owned and reassign each one.
    • Remove their paid seats, not only their access.
    • Move any billing email that pointed to their personal inbox.

    A lightweight approval rule for new tools

    Keep the rule short so people follow it. A workable version: anyone can start a free trial, but a tool only becomes paid once it has an owner, a tool group and a row in the register. For tools that will hold company or customer data, add a basic security check. CISA’s fact sheet on assessing vendors points small businesses to a standard set of questions you can borrow from.

    Payment setups compared

    The register tells you what you pay for. How you pay decides how fast you see problems and how far an overrun can go.

    SetupVisibilityOverrun riskIf the card fails or is compromised
    Founder’s personal cardMixed with personal spendingNo ceiling beyond the card limitEvery tool fails, plus personal payments
    One company card for all toolsLong mixed statementLimited only by the card limitEvery tool fails at once
    Employees pay and claim backArrives late, in expense reportsHard to see until claims arriveEach person’s card is separate
    One prepaid card per tool groupEach card’s charges belong to one groupCapped by the balance loadedOnly that group’s tools are affected

    Using prepaid cards per tool group

    A prepaid card can only spend what is loaded onto it. If the design tools group has a quarterly budget, load that amount onto the design card. When the balance runs low, that is your signal to review, not a bill you discover later. A new tool someone signs up for cannot quietly double the group’s spend, because the card simply declines.

    Two rules make this work. First, keep the number of cards small: one per tool group, not one per tool, unless a single tool is large. Second, record each card’s last four digits in the register so every charge maps to a group automatically.

    Worked example with Vizovcc

    Vizovcc is one way to run this setup. It sells prepaid virtual Visa and Mastercard cards that you buy from one account balance funded with crypto such as USDT, USDC, Bitcoin or ETH. You can hold several cards in one account, each with its own loaded balance, and freeze or unfreeze any card from the dashboard. Every card supports 3D Secure, and card pages show which ones work with Apple Pay and Google Pay.

    For a remote team, a simple layout would be one Vizovcc card for design tools, one for engineering tools, one for AI subscriptions and one for admin software. Each card page shows the card’s price and how it splits between the issue charge and the balance loaded onto the card, so you can match a card to a group budget. If a tool group is under review, freezing its card stops new charges until the owner decides.

    Be clear about the limits. Vizovcc has no team roles, sub-accounts or employee card issuance, and you cannot set spend limits or merchant locks on a card. Whoever signs in sees every card, so keep the account with one finance owner and let them add cards to tools. Each software vendor also decides which cards it accepts, and any merchant can decline a prepaid card, so test a new card on a smaller tool first. Vizovcc’s page on prepaid Visa and Mastercard cards covers software payments and declined charges in more detail.

    Common questions

    How many tool groups should a small team have?

    Usually four to six. Fewer than that and groups get too broad to review; more and you spend time managing cards instead of tools.

    Who should own the software register?

    One operations or finance person keeps the file, but each tool has its own owner. The file keeper chases owners; owners make the keep or cancel decisions.

    Should employees ever pay for tools themselves?

    For one-off purchases, reimbursement is fine. For anything recurring, move it to a company payment method so renewals appear in your review and not in someone’s expense claim months later.

    What about annual plans that are cheaper?

    Take them for tools you are confident about, but log the renewal date and set a reminder 45 days ahead. Annual plans are where most surprise charges come from.

    Key takeaways

    • Surprise software charges come from missing ownership, not from one bad decision.
    • A ten-column register and a 30-minute monthly check catch most problems.
    • Offboarding should remove paid seats and move billing emails, not only access.
    • One prepaid card per tool group adds a hard ceiling and makes every charge traceable.
    • Budgets still need a human review: a card balance is a signal, not a strategy.

    Start this week by exporting three months of card statements and filling the register. Once every tool has an owner, you can decide whether separate cards per tool group would help. If you want to try that approach with prepaid cards funded by crypto, take a look at Vizovcc and compare its card pages with your group budgets.

  • Choosing a Virtual Card Provider: 12 Questions to Ask

    Choosing a Virtual Card Provider: 12 Questions to Ask

    Consider a typical story (an example, not a real company). A small agency signs up with the first virtual card provider it finds because the issue fee looks low. Three months later it holds 30 cards and pays a monthly fee on each one, a foreign transaction fee on every ad charge, and a withdrawal fee to get unused money back. Then a client’s ad account starts declining payments because the platform asks for a 3-D Secure code the provider cannot pass through. None of this was hidden. Nobody asked.

    Virtual card providers look alike on their homepages. The differences sit in fee schedules, funding rules, card types and what happens when something goes wrong. If you are working out how to choose a virtual card provider, the fastest route is to ask every candidate the same questions and compare the answers side by side. Here are the 12 that matter most, why each one matters and what a weak answer looks like.

    Before you start: write down your use case

    Answers only mean something against your own needs. Spend ten minutes listing:

    • What you will pay for: subscriptions, ad accounts, cloud bills, suppliers or one-off purchases.
    • How many cards you expect to hold in six months.
    • Which currencies your vendors bill in.
    • Who on your team needs access, and to what.
    • Whether you need cards in person, or only online.

    The 12 questions

    1. Is the card credit, debit, charge or prepaid? This decides whether you need a credit review, whether you can overspend, and which merchants will take it. Google Ads, for example, does not accept prepaid cards for automatic postpay billing.
    2. What is the full fee schedule? Ask for every fee in writing: issue fee, monthly or annual fee, per-transaction fee, foreign exchange fee, deposit fee, withdrawal fee and decline fee. Then multiply by the number of cards you plan to hold.
    3. How do I fund the account, and how do I get money back out? Funding options range from bank transfer to cards to crypto. Withdrawal terms matter just as much: minimums, fees, review times and the methods available.
    4. What identity checks are required, and when? Most legitimate providers verify customers. Ask what documents are needed, whether checks happen before the first card, and how documents are stored.
    5. Which networks, countries and currencies are available? A card in the vendor’s billing currency avoids a conversion on every charge. Some merchants also accept some networks or issuing countries but not others.
    6. Will my merchants accept these cards? No provider can guarantee acceptance, because each merchant decides. A good provider says so plainly and explains common decline causes. Plan to test each card with a small payment.
    7. Which card types do you issue? Single-use numbers suit one-off purchases. Multi-use cards suit subscriptions and ad accounts. Ask whether a card can be reloaded, and how.
    8. What controls exist on each card? Some providers offer per-card spending limits, merchant locks or a freeze button. Others rely on a prepaid balance as the only ceiling. Neither is wrong, but you should know which you are getting.
    9. How does team access work? Ask about roles, sub-accounts and audit logs. If there are none, everyone who signs in sees every card, which shapes who should hold the login.
    10. How long does issuing take, and what happens if a card cannot be issued? Be wary of vague promises of instant cards. More useful is a clear answer on refunds when an order fails.
    11. How long are cards valid? Every expiry means updating payment details on live accounts. Longer validity means fewer interruptions.
    12. How do you handle declines, 3-D Secure and support? Ask whether the provider can complete 3-D Secure checks, which support channels exist, and what to do if card details leak.

    Strong answers vs red flags

    TopicA strong answerA red flag
    FeesA complete, published fee table“Fees vary” with no schedule
    AcceptanceStates that merchants decide and lists decline causesGuarantees acceptance everywhere
    Identity checksExplains what is checked and whenPromises no verification at all
    WithdrawalsClear minimums, fees and methodsNo way to get unused funds back
    Failed ordersFull refund to your balanceNo stated policy
    Use policyLegitimate spend only, platform rules applyMarkets cards as a way around bans or reviews

    How to score providers

    1. Mark your must-haves. From your use case, pick the three or four questions that would rule a provider out, such as currency, card type or team access.
    2. Ask every candidate in writing. Use their help pages, FAQ and support email, so you have the answers on record.
    3. Model a full year of costs. Use your expected card count and monthly transactions, not a single card.
    4. Run a small test. Buy one card, add it to one merchant, and complete one payment before moving real budgets.
    5. Decide on fit, not features. The provider with the longest feature list is not always the best match for how you pay.

    A worked example: ZenVCC’s answers

    To show what a set of answers looks like, here is how ZenVCC, a prepaid virtual card platform, answers the 12 questions based on its own website. The point is the format, not a recommendation for every reader.

    QuestionAnswer
    1. Card typePrepaid virtual Visa, Mastercard, American Express and Maestro cards. Not a bank, no credit line.
    2. Fees$10 one-time issue fee per card, $0.10 per card payment, no monthly fee. Any deposit charge is shown before paying.
    3. Funding and withdrawalsFunded with Bitcoin, USDT (TRC-20 or Solana), TRX or SOL, each deposit checked on its blockchain. Balance withdrawals are in crypto, minimum $10, no withdrawal fee, reviewed before sending.
    4. Identity checksMay ask you to verify your identity before buying a card.
    5. Networks and countriesAbout 49 cards, including USA, Turkey, Argentina, China, Egypt and Portugal cards, plus local-currency cards.
    6. AcceptanceEach platform decides; acceptance is not guaranteed.
    7. Card typesMulti-use prepaid cards. No single-use numbers, and cards can’t be topped up from the dashboard.
    8. ControlsNo per-card limits, merchant locks or freeze. The prepaid balance is the ceiling; budgets are set inside each platform.
    9. Team accessOne sign-in, no roles or sub-accounts. A separate card per teammate, project or vendor from one balance.
    10. Issuing and failed ordersCards show as processing until ready; no issue time is stated. If a card can’t be prepared, the full amount returns to the balance.
    11. ValidityThree years from the day the card is ready.
    12. Declines and supportPayments that need a 3-D Secure code can’t be completed with these cards. Support is by email.

    Read against the scoring steps, this profile suits teams that want one prepaid card per vendor or ad account, predictable fees and no credit review, and that are comfortable funding with crypto. It is a weaker fit for anyone who needs per-card limits, multiple user roles or merchants that require 3-D Secure. You can check the details yourself in ZenVCC’s FAQ, which also covers verification documents and what to do if card details leak.

    Key takeaways

    • Write down your use case first; answers only make sense against your own needs.
    • Ask every provider the same 12 questions in writing and compare them side by side.
    • Model a full year of fees across all the cards you plan to hold.
    • Treat guaranteed acceptance or “no verification” as warning signs, not selling points.
    • Test with one card and one payment before you move real budgets.

    Copy the 12 questions into a spreadsheet, add a column for each provider on your shortlist, and fill it in before you sign up anywhere. If a prepaid, per-vendor setup matches your needs, add ZenVCC as one of the columns and see how it compares.

  • Card-Not-Present Fraud: How Virtual Cards Change the Odds for Online Shoppers

    Card-Not-Present Fraud: How Virtual Cards Change the Odds for Online Shoppers

    A $1.00 charge from a merchant you’ve never heard of, then a $480 one an hour later. Your physical card never left your wallet. Someone had your number, expiry date and security code, and that is all an online checkout needs.

    Quick answer

    1. Card-not-present (CNP) fraud uses stolen card details, not the card itself. The details leak through breaches, skimming scripts on checkout pages, phishing and malware.

    2. Virtual cards don’t stop the theft. They limit the damage: one card per merchant, a capped balance, and a freeze switch.

    3. They also move the risk. The dashboard that holds your card details becomes the thing you most need to protect.

    How card details get stolen

    CNP fraud starts with a data leak. The main routes are:

    • Merchant breaches. Attackers get into a merchant’s systems and copy stored payment data or order records. PCI DSS rules forbid merchants from storing the CVV2 after authorization, but card numbers, expiry dates and billing addresses can still be exposed, especially at smaller merchants.
    • E-skimming (Magecart-style attacks). Malicious JavaScript is injected into a checkout page and copies what you type, including the CVV, as you type it. The merchant’s site looks normal, and the order goes through.
    • Phishing. Fake delivery notices, “payment failed” emails and lookalike login pages ask you to re-enter card details.
    • Infostealer malware. Malware on your device harvests saved browser card data and session cookies.
    • Card testing and enumeration. Bots try number, expiry and CVV combinations against weakly protected checkouts with tiny charges. A $1 authorization that succeeds tells them the card is live.

    The last one explains the opening example. A small test charge followed by a larger purchase is the classic CNP pattern. The test confirms the card works, and the real fraud comes next.

    What the card networks already do

    Several layers sit between stolen details and a successful fraudulent charge:

    • CVV2 proves the person paying has seen the card details. It stops some attacks, but not skimming or phishing, which capture the CVV too.
    • AVS compares the billing address entered with the one the issuer holds. It helps mostly in the US, UK and Canada.
    • 3D Secure 2 sends device and transaction data to the issuer, which can approve quietly or challenge the shopper with a one-time code. Where 3DS authenticates a payment, fraud liability generally shifts from the merchant to the issuer.
    • Issuer fraud models score each authorization for unusual merchants, amounts, locations and velocity.

    These layers catch a lot. They miss whatever looks normal: a plausible amount, at a plausible merchant, with correct details.

    What a virtual card changes, and what it doesn’t

    A virtual card is a card number issued without plastic, usually managed from a dashboard. Here is how it compares, attack by attack.

    AttackWhat a virtual card changesWhat it doesn’t change
    Merchant breachIf the card is used only at that merchant, the leak exposes one card. Freeze it and issue another.The leaked card is still valid until you act.
    E-skimming on checkoutDamage is capped by the balance on that one card.The skimmer still captures the details.
    Phishing for card detailsA low-balance card limits what the attacker can spend.You can still be tricked into typing details or a 3DS code.
    Card testingSmall unknown charges stand out on a single-purpose card.Bots can still test numbers on the card’s BIN range.
    Merchant account takeoverOne card per merchant contains the loss to that card.The attacker can still spend up to the balance through your stored card.
    Dashboard account takeoverNothing. This is the new risk.Whoever controls the dashboard sees every card number and CVV.

    The pattern is clear. A virtual card shrinks the blast radius of a leak and makes the leak easier to spot. It doesn’t prevent a leak, and it adds one high-value target: the account that issues the cards.

    Three design choices that change the odds

    One card per merchant. If each subscription and store gets its own card, a breach at one merchant exposes one card. An unfamiliar charge on the card you use only for a streaming service is obviously fraud, and you don’t need to reissue every card you own.

    A capped balance. On a prepaid card, the balance is the maximum loss. A card holding $40 for a monthly subscription can’t fund a $480 fraudulent purchase. That is a stronger control than a credit limit, which is often far larger than what you need.

    A freeze switch. Cards for occasional purchases can stay frozen between uses. Fraudulent authorizations on a frozen card are declined before they settle.

    What about disputes? Dispute and chargeback rights depend on the issuer, the network rules and the card type. Prepaid card protections vary by program, so ask your provider how it handles unauthorized transactions before you rely on them.

    One worked example

    As an example of how these controls look in practice, VCCBuy issues prepaid virtual Visa and Mastercard cards funded with stablecoins and other crypto. Each card can be frozen and unfrozen, renamed, given its own saved billing name and address, and checked through its own transaction list. Unspent balance can be withdrawn to a crypto wallet. 3D Secure codes are requested on the card in the dashboard and shown for 10 minutes. No phone number is involved, so a SIM-swap attack can’t intercept them. It also means the dashboard login carries the security weight that a phone would normally share.

    The limits are worth stating. Some merchants decline prepaid cards. VCCBuy is not a bank, and its cards are for online use only. Bank-issued virtual cards, browser-based card tokens and merchant-specific numbers from your existing bank offer similar compartmentalization, and many readers already have access to one of them.

    Securing the account that holds your cards

    Because the dashboard is now the master key, harden it first.

    1.  Use a unique, long password stored in a password manager. Never reuse the password from your email or exchange account.

    2.  Turn on any extra sign-in protection the provider offers, and secure the email account linked to it, since email resets are the usual route into accounts.

    3.  Bookmark the real login page and use only that bookmark. Never sign in from a link in an email or chat message.

    4.  Never read a 3DS code to anyone. No genuine support agent, bank or merchant will ask for one. A caller asking for “the code we just sent” is trying to approve a payment you didn’t make.

    5.  Keep the device clean. Update the browser and operating system, and don’t save card details in browser autofill on shared or work machines.

    6.  Review transactions weekly. Look specifically for small authorizations from unfamiliar merchants, which are often card tests.

    Shopper’s CNP checklist

    ☐  One virtual card per merchant or subscription

    ☐  Balance on each card sized to its expected charges

    ☐  Occasional-use cards frozen between purchases

    ☐  Card names that show which merchant each one belongs to

    ☐  Unique password and the strongest available sign-in protection on the card dashboard

    ☐  Linked email account secured

    ☐  3DS codes never shared, under any story

    ☐  Weekly scan for small, unfamiliar charges

    ☐  A plan for a leak: freeze, reissue, update the merchant, report

    FAQ

    Are virtual cards immune to card-not-present fraud? No. A virtual card number can be skimmed, phished or leaked in a breach like any other. The difference is containment. A single-merchant, low-balance card limits how much a thief can spend and makes the fraud easy to spot and shut down.

    What does a $1 charge from an unknown merchant mean? Often a card test: someone checking that stolen details work before making a larger purchase. Freeze the card, report the charge to your provider and replace the card. Don’t wait to see if a bigger charge follows.

    Is a prepaid virtual card safer than a credit card online? It depends on the threat. A prepaid card caps losses at the balance, which helps against breaches and skimming. A credit card may offer stronger dispute rights, depending on the issuer and your country. Many people use both: credit for large purchases, prepaid virtual cards for subscriptions and unfamiliar merchants.

    Conclusion

    Card-not-present fraud is a data problem. Your details will leak somewhere eventually, so the useful question is how much a leak can cost and how fast you’ll notice it. One card per merchant, a lean balance and a well-protected dashboard change those odds a great deal. VCCBuy is one way to build that setup with crypto funding, and your own bank’s virtual cards may be another.

    About the author: [Author name] is a payments and fintech writer at VCCBuy (https://vccbuy.net/), where they cover virtual cards, card networks and spending stablecoins online. They write about card fraud mechanics and practical ways shoppers can limit their exposure.

    Disclosure: the author writes for VCCBuy, which is mentioned in this article.

  • SAP Cloud Platform Integration: Security and Authentication Guide

    SAP Cloud Platform Integration: Security and Authentication Guide

    SAP Cloud Platform Integration, now part of SAP Integration Suite, provides integration capabilities for connecting SAP and non-SAP applications across cloud, on-premise, and hybrid environments. Security and authentication are essential because integration flows can exchange business data between systems such as SAP S/4HANA, SAP SuccessFactors, SAP Ariba, Salesforce, databases, APIs, and external services.

    A secure integration architecture controls who can access an integration service, which systems can communicate, how messages are authenticated, and how sensitive information is protected.

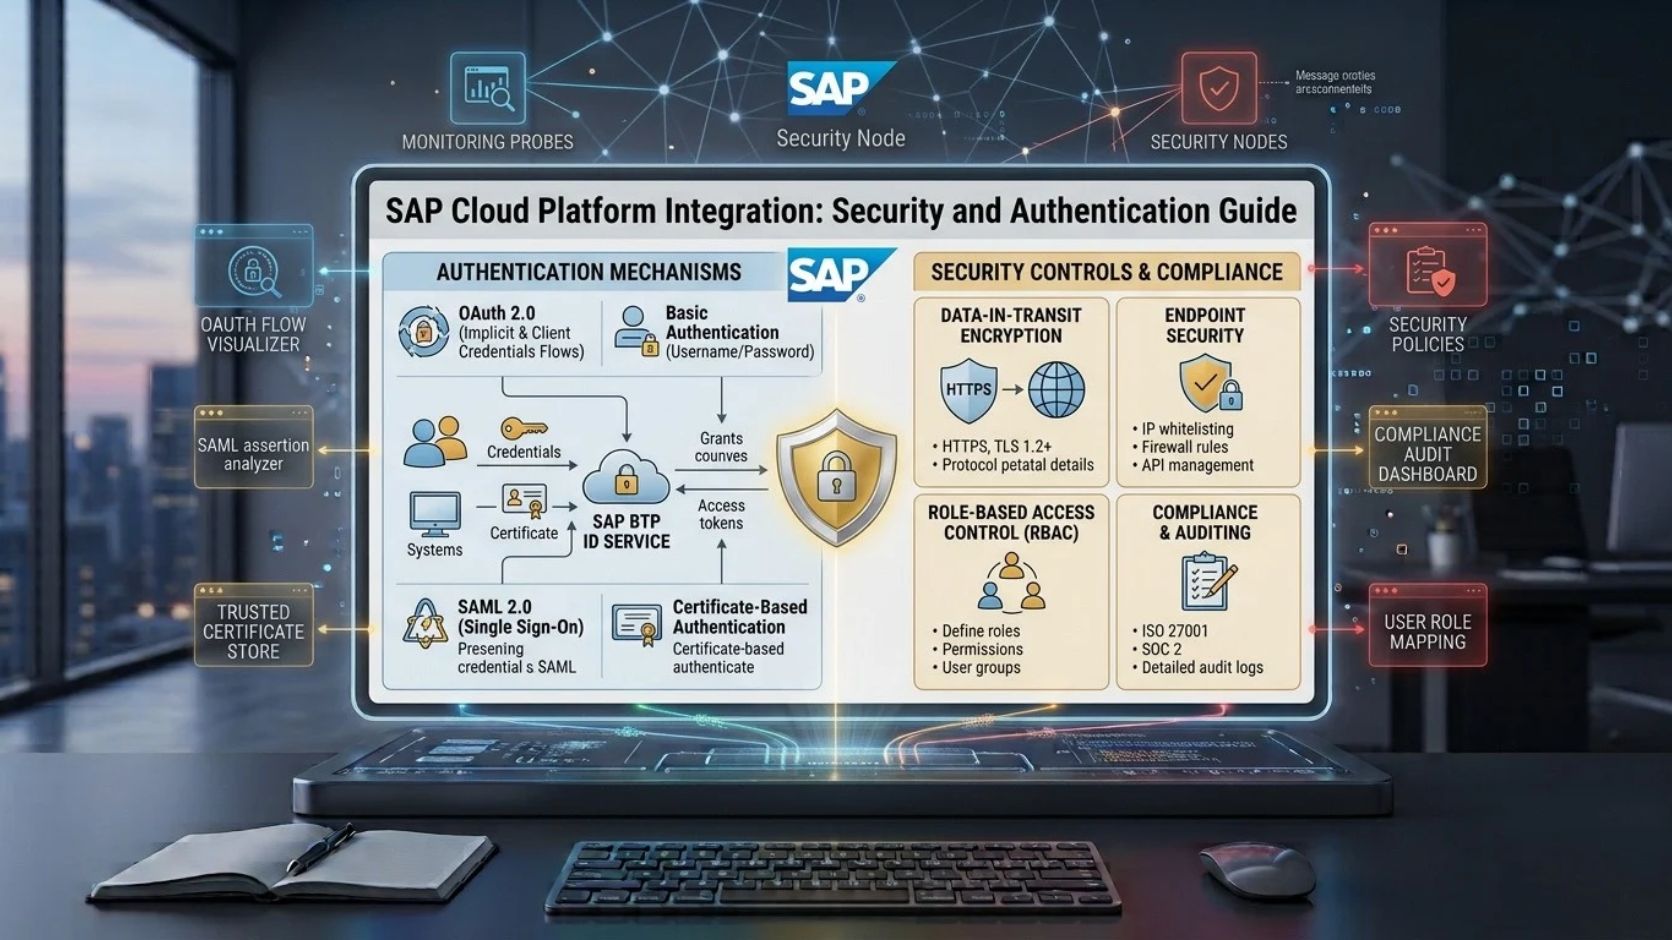
    SAP Cloud Integration supports several authentication and security mechanisms. These can include OAuth 2.0, client certificates, basic authentication, SSH keys, and other supported security configurations, depending on the integration scenario and adapter.

    Destinations can also be used in relevant SAP environments to manage connection information for applications and services. A destination may contain endpoint information, authentication configuration, and other connection properties.

    What Is Security in SAP Cloud Platform Integration?

    Security in SAP Cloud Platform Integration covers the controls used to protect integration flows, APIs, credentials, messages, endpoints, and connected applications.

    An integration platform can act as a central communication layer between many systems. This makes security important at multiple points.

    For example:

    S/4HANA → Cloud Integration → Salesforce

    In this architecture, Cloud Integration must securely communicate with both the sender and receiver. The integration flow may also transform business information before sending it to the target application.

    Security therefore includes authentication, authorization, encryption, credential management, certificate management, network protection, and secure monitoring.

    Why Security and Authentication Matter

    Enterprise integration can involve sensitive business information such as customer records, financial transactions, employee data, supplier information, sales orders, invoices, and inventory details.

    Unauthorized access could expose or modify this information.

    Authentication confirms the identity of a user, system, or application. Authorization determines what that authenticated identity is allowed to access.

    These two concepts are different.

    For example, an application may successfully authenticate with an API but still receive a 403 Forbidden response because it does not have permission to access a particular resource.

    A secure integration design must therefore address both authentication and authorization.

    Authentication vs Authorization

    Authentication answers the question:

    “Who or what is requesting access?”

    Authorization answers:

    “What is that identity allowed to access?”

    An application may use OAuth 2.0 to authenticate against an API. The API can then use scopes or other access controls to determine which resources the application can use.

    Similarly, an S/4HANA integration may require a technical user or another supported identity with specific permissions.

    Using authentication without appropriate authorization controls does not provide complete access protection.

    Common Authentication Methods in SAP Cloud Integration

    The appropriate authentication method depends on the connected system, adapter, interface, security requirements, and SAP architecture.

    Common methods include:

    OAuth 2.0: Used for token-based authorization and access to supported APIs and services.

    Basic Authentication: Uses a username and password. It is generally used only where the target service supports it and where secure transport is configured.

    Client Certificate Authentication: Uses digital certificates to establish trust between systems.

    SSH Authentication: Commonly used for secure file transfer scenarios such as SFTP, often using SSH keys.

    The selected method should match the security capabilities of the target application.

    OAuth 2.0 in SAP Cloud Integration

    OAuth 2.0 is a widely used authorization framework for API-based communication.

    Instead of sending a username and password with every API request, an application can obtain an access token from an authorization server and use that token to access protected resources.

    A simplified process is:

    Client → Authorization Server → Access Token → API

    The token provides the access required by the API according to the configured authorization rules.

    OAuth 2.0 configurations can involve client IDs, client secrets, scopes, token endpoints, and access tokens. Exact requirements depend on the service provider.

    Access tokens should be treated as sensitive security information and should not be exposed unnecessarily in logs or message payloads.

    Basic Authentication

    Basic Authentication sends a username and password as part of an HTTP authentication mechanism.

    When used over HTTPS, the communication channel is encrypted during transmission. However, Basic Authentication still requires careful credential management.

    Passwords should not be placed directly inside integration-flow logic or exposed through logs.

    Where a stronger authentication mechanism is supported and required by the target system, organizations may use alternatives such as OAuth 2.0 or certificate-based authentication.

    Client Certificate Authentication

    Client certificates can provide certificate-based authentication between communicating systems.

    A certificate identifies the client and participates in establishing a trusted secure connection.

    Certificate-based authentication is commonly used when strong machine-to-machine authentication is required.

    Certificate management includes key generation, certificate installation, trust configuration, expiration monitoring, and renewal.

    An expired certificate can cause an integration to fail even when the integration flow itself has not changed.

    SFTP and SSH Authentication

    File-based integrations frequently use SFTP, which operates through SSH.

    An SFTP connection can use username/password authentication or SSH key-based authentication depending on the server and integration configuration.

    SSH keys are commonly used for automated system-to-system file transfer because they avoid the need to store a traditional password for every automated connection.

    The private key must be protected carefully. It should not be exposed in source code, logs, or message content.

    HTTPS and Transport Encryption

    HTTPS uses TLS to protect data while it travels between systems.

    Encryption helps prevent unauthorized parties from reading or modifying data during network transmission.

    For API and HTTP-based integrations, HTTPS should be used when supported and required by the security architecture.

    TLS configuration can also involve server certificates and trust relationships.

    A certificate problem may cause connection failures when the client cannot establish trust with the server.

    Trust Configuration and Certificates

    Certificates are an important component of secure enterprise integration.

    A certificate can establish trust between the integration platform and a remote server or client.

    Certificate-related problems may occur when:

    • A certificate has expired.
    • A certificate is not trusted.
    • The certificate chain is incomplete.
    • The hostname does not match the certificate.
    • A required client certificate is missing.
    • The wrong certificate is configured.

    Certificate validity should be monitored before expiration to reduce unexpected integration failures.

    Destinations and Authentication

    Destinations provide connection information for accessing services and applications in supported SAP environments.

    A destination can contain information such as the target URL, authentication type, and connection properties.

    For example, an application may use a destination to identify an S/4HANA API endpoint without embedding the endpoint and authentication configuration directly into application code.

    This separation can make connection management easier when environments change.

    Development, testing, and production environments often use different endpoints. The appropriate destination configuration must therefore point to the correct environment.

    Secure Management of Destinations

    Destinations should be configured according to the security requirements of the connected application.

    Sensitive information should not be exposed unnecessarily. Access to destination configuration should be limited to authorized users and services.

    When a destination uses credentials, certificates, or OAuth-related information, the security of those credentials becomes part of the overall integration security architecture.

    A change to a destination can affect every application or integration flow that depends on it. Changes should therefore be controlled and tested.

    Authorization in SAP Cloud Integration

    Authorization determines what a user or technical identity can do after authentication.

    Cloud Integration environments can use role-based access controls to restrict administrative and development functions.

    Different users may need different permissions. A developer may require integration-flow development access, while an operations user may primarily need monitoring access.

    Applying appropriate roles reduces unnecessary access to integration artifacts and runtime information.

    The exact roles and permissions depend on the SAP BTP environment, subscription, services, and configured security architecture.

    Role-Based Access Control

    Role-based access control assigns permissions based on defined roles.

    For example, access to development functions can be separated from operational monitoring functions.

    This supports the principle of least privilege, where users and technical identities receive only the permissions required for their tasks.

    Administrative access should be limited because administrative functions can affect integration flows, security settings, credentials, and runtime behavior.

    Secure Credential Management

    Credentials are one of the most important security elements in an integration environment.

    Passwords, client secrets, private keys, tokens, and certificates should be managed through appropriate secure mechanisms.

    Credentials should not be hard-coded into scripts or integration messages.

    When credentials need to be rotated, the related configuration should be updated without exposing the new credential to unauthorized users.

    Credential rotation is particularly important for long-running enterprise integrations.

    API Security

    API-based integration requires protection at the API layer as well as the integration platform.

    API security can involve authentication, authorization, rate controls, input validation, TLS encryption, and monitoring.

    For example, an S/4HANA API may require OAuth-based access and specific permissions.

    Cloud Integration can act as an intermediary that receives a message, validates or transforms the data, and calls the target API.

    API credentials and tokens should not be written to logs or exposed through error responses.

    Security for SAP S/4HANA Integration

    S/4HANA integration may involve OData, REST, SOAP, IDoc, and other interfaces.

    Each interface can have different security requirements.

    For example, an OData service may use HTTPS and an authentication mechanism supported by the S/4HANA environment. An IDoc scenario may require a different technical configuration.

    For on-premise S/4HANA systems, secure connectivity between the internal network and cloud services must also be considered.

    A hybrid architecture can look like:

    S/4HANA On-Premise → Secure Connectivity → Cloud Integration → External Application

    Security must be maintained across each connection in this architecture.

    Security for Cloud-to-Cloud Integration

    Cloud-to-cloud integrations connect services that operate outside a traditional internal network.

    For example:

    S/4HANA Cloud → Cloud Integration → Salesforce

    Each application may use its own identity provider, API authentication method, certificates, or authorization model.

    Cloud Integration must therefore be configured to meet the requirements of both systems.

    Using HTTPS, OAuth 2.0, certificates, secure credentials, and appropriate authorization can help protect the communication path.

    Security for Hybrid Integration

    Hybrid integration connects cloud applications with on-premise systems.

    Security considerations include network connectivity, authentication, certificates, firewall rules, identity management, and authorization.

    A secure connectivity component may be used to establish communication between cloud services and internal applications.

    The architecture should prevent unauthorized external access to internal systems while allowing required business communication.

    Data Protection in Integration Flows

    Integration flows can process large amounts of business information.

    Data protection should consider what information is collected, transformed, transmitted, logged, and stored during processing.

    Sensitive information should only be processed when required for the business process.

    Message logging should be controlled carefully. Full message payload logging may expose customer data, financial information, personal information, or other confidential content.

    Where detailed logging is required for troubleshooting, organizations should apply appropriate data protection and access controls.

    Security Risks in Integration

    Common integration security risks include exposed credentials, weak authentication, excessive permissions, unsecured endpoints, expired certificates, insufficient logging controls, and unauthorized access to integration artifacts.

    Hard-coded passwords are particularly risky because they can remain inside source files or configuration artifacts.

    Another risk is giving a technical user more permissions than required.

    Security reviews should therefore examine both the integration platform and every connected system.

    Security Monitoring and Error Handling

    Security monitoring is closely connected to operational monitoring.

    A failed authentication attempt can indicate an incorrect configuration, an expired credential, or an unauthorized access attempt.

    For example, repeated 401 Unauthorized responses may indicate authentication problems. Repeated 403 Forbidden responses may indicate authorization problems.

    Integration teams should distinguish between normal configuration errors and suspicious access patterns.

    Error messages should also avoid exposing passwords, tokens, private keys, or other sensitive security information.

    Secure Integration Development

    Security should be considered during integration design and development.

    Integration developers should select appropriate authentication mechanisms, protect credentials, validate incoming data, avoid unnecessary logging, and apply suitable authorization controls.

    Testing should include successful authentication as well as invalid credentials, expired certificates, missing permissions, invalid tokens, and unauthorized requests.

    Security testing should also verify that error messages do not expose confidential information.

    Security Testing Before Production

    Before deploying an integration flow to production, security-related scenarios should be tested.

    For example, testing can verify that an invalid credential is rejected, an unauthorized user cannot access restricted resources, and an expired certificate produces an identifiable error.

    API access should be tested with valid and invalid tokens where the testing environment supports it.

    Destination configurations should also be verified to ensure that the correct endpoint, authentication method, and environment are being used.

    Testing should not rely only on successful business transactions. Failure scenarios are also important.

    Security Best Practices for SAP Cloud Integration

    A secure implementation should use supported authentication mechanisms, encrypted transport, controlled access, and secure credential management.

    Permissions should be limited according to job responsibilities. Integration flows should not contain hard-coded passwords or private security information.

    Certificates and credentials should have defined renewal and rotation processes.

    Destinations should be reviewed when endpoints, credentials, certificates, or authentication mechanisms change.

    Logs should contain enough information for troubleshooting without exposing unnecessary sensitive data.

    Security configuration should also be reviewed when integrations are moved between development, test, and production environments.

    Frequently Asked Questions

    What is SAP Cloud Platform Integration security?

    SAP Cloud Platform Integration security includes authentication, authorization, encryption, certificate management, credential protection, secure connectivity, access control, and monitoring.

    What authentication methods does SAP Cloud Integration support?

    Depending on the integration scenario, supported authentication mechanisms can include OAuth 2.0, Basic Authentication, client certificates, SSH authentication, and other adapter-specific methods.

    What is OAuth 2.0 used for in SAP Cloud Integration?

    OAuth 2.0 is used for token-based authorization when accessing supported protected APIs and services. It allows applications to use access tokens instead of sending a username and password with every request.

    What are Destinations in SAP integration?

    Destinations provide connection information for applications and services in supported SAP environments. They can contain information such as a target URL, authentication configuration, and connection properties.

    Can Destinations contain authentication information?

    Yes. Depending on the destination type and configuration, authentication-related information can be associated with a destination. Sensitive credentials should always be protected through the supported security mechanisms.

    How does SAP Cloud Integration protect data during transmission?

    HTTPS and TLS can encrypt data during network transmission. Other secure protocols, such as SFTP over SSH, can provide encrypted communication for file-based integrations.

    What is the difference between authentication and authorization?

    Authentication verifies an identity. Authorization determines what that identity is permitted to access or perform.

    How are certificates used in SAP Cloud Integration?

    Certificates can establish trust and support secure authentication between systems. They can be used for server trust and, where configured, client certificate authentication.

    How can S/4HANA be securely connected to Cloud Integration?

    The appropriate architecture depends on whether S/4HANA is cloud or on-premise. Secure APIs, HTTPS, authentication mechanisms, certificates, and secure connectivity components can be used according to the deployment and interface requirements.

    Why is secure credential management important?

    Credentials such as passwords, client secrets, tokens, and private keys provide access to systems and services. If they are exposed, unauthorized parties may gain access to protected resources.

    Conclusion

    SAP Cloud Platform Integration security requires protection across the complete integration lifecycle. Authentication establishes the identity of users and systems, while authorization controls the resources they can access.

    OAuth 2.0, certificates, HTTPS, SFTP, SSH, Basic Authentication, role-based access, and secure credential management can be used according to the integration scenario. Security requirements vary between S/4HANA, SAP applications, third-party platforms, APIs, and on-premise systems.

    Destinations can support secure connection management in relevant SAP environments by providing endpoint and authentication configuration. Correct destination configuration is particularly important when integrations use different development, testing, and production environments.

    A secure Cloud Integration architecture also requires controlled access, protected credentials, certificate management, appropriate logging, secure APIs, and regular security testing. These controls help protect business data while maintaining reliable communication between SAP and external applications.
  • Crypto-Funded Virtual Cards: How On-Ramps Connect Digital Assets to Card Networks

    Crypto-Funded Virtual Cards: How On-Ramps Connect Digital Assets to Card Networks

    Crypto-funded virtual cards translate digital asset balances into spendable fiat at the point of use. Their core function depends on on-ramps that handle conversion, compliance, and settlement across card networks. This structure reduces friction between crypto wallets and conventional payments while preserving a familiar checkout experience. The model appears simple on the surface, yet its operational chain involves several critical mechanisms that determine speed, cost, and reliability.

    What Are Crypto-Funded Virtual Cards?

    At a functional level, crypto-funded virtual cards are digital payment cards linked to a cryptocurrency balance and used for online or card-not-present transactions. They typically exist within digital wallets or issuer apps, presenting card credentials without requiring a physical card. Their purpose is to let holders spend crypto-derived value in familiar e-commerce environments while maintaining transaction security controls comparable to conventional virtual cards.

    From an analytical perspective, their design emphasizes user experience, configurable spending limits, and seamless tech integration with merchant payment systems.

    However, cryptocurrency volatility can affect available balances and purchasing predictability, influencing both consumer behavior and issuer risk management.

    Broader market adoption depends on regulatory clarity, interoperability, and consumer education, since understanding custody, fees, and security practices remains essential to informed usage and trust.

    How Do Crypto On-Ramps Work?

    How, then, do crypto on-ramps convert conventional money into spendable digital assets? They typically connect bank transfers, cards, or payment apps to a regulated exchange or processor. After identity verification and compliance screening, fiat funds are accepted, priced, and exchanged for selected cryptocurrencies, then delivered to a custodial or external wallet.

    Effective design emphasizes user experience while embedding security measures throughout onboarding and settlement.

    • Identity checks confirm eligibility, jurisdiction, and anti-money-laundering compliance.
    • Pricing engines source rates, calculate fees, and execute conversions efficiently.
    • Wallet delivery mechanisms route purchased assets to designated addresses or accounts.

    Operational reliability depends on banking partnerships, liquidity providers, and transaction monitoring.

    Together, these components create a standardized path from conventional payment rails into blockchain-based balances, without yet addressing downstream card-based spending mechanics or merchant settlement processes.

    How Do Crypto Cards Convert Wallet Balances?

    When a crypto-funded card is presented for payment, the issuer or program manager typically checks the linked wallet balance, determines the amount of digital assets required, and initiates a conversion into the fiat currency needed for authorization and settlement.

    This conversion framework depends on wallet integration, pricing logic, and predefined liquidation rules. The platform may source exchange rates from internal inventories, partner exchanges, or liquidity providers, then apply spreads, fees, and risk controls before calculating the exact asset quantity to sell.

    Balance synchronization is essential, because wallet data, pending transfers, and network confirmations affect what amount is actually available for conversion. Some programs pre-fund fiat accounts and later replenish them through asset sales, while others execute just-in-time conversion.

    In both models, automation minimizes manual intervention and supports consistent funding availability.

    What Happens During a Crypto Card Payment?

    A crypto card payment typically begins with authorization, during which the issuer verifies the available wallet balance and transaction parameters.

    If approved, the required crypto amount is converted into fiat at the applicable exchange rate to satisfy the merchant-facing payment request.

    The transaction then proceeds through standard card network settlement, where funds are cleared and transferred within the conventional payments infrastructure.

    Authorization And Balance Check

    Initiating a crypto-funded card payment triggers an authorization sequence in which the merchant’s payment terminal sends the transaction details through the card network to the issuing provider.

    The provider evaluates predefined authorization methods and performs balance verification against the cardholder’s available crypto-linked funding source, applying risk rules, spending limits, and account status checks before approving or declining.

    • Merchant data, amount, and merchant category code are transmitted for review.
    • The issuer checks wallet linkage, available value, and fraud controls.
    • A response code returns through the network to the merchant within seconds.

    This stage is strictly about confirming funding sufficiency and transaction validity. It determines whether the payment can proceed, while preserving the familiar card-network experience expected by merchants, gateways, acquirers, and point-of-sale systems and consumers alike worldwide.

    Crypto-To-Fiat Conversion

    Following authorization, the transaction enters the conversion stage, where the crypto-linked funding source is translated into the fiat amount required for card-network settlement.

    The issuer or on-ramp provider calculates the exact debit needed, referencing current exchange rates, fee schedules, and any spread applied to the customer.

    At this point, conversion logic determines whether assets are sold instantly, drawn from prefunded fiat reserves, or netted against internal inventory.

    Effective liquidity management is essential, because providers must satisfy payment timing while minimizing slippage and operational exposure.

    Controls also account for market volatility, which can alter execution prices between authorization and conversion.

    Some programs use buffers, hedging, or stablecoin balances to reduce this risk.

    The result is a finalized fiat-equivalent obligation assigned to the cardholder’s crypto-funded account for accurate transaction posting.

    Card Network Settlement

    Once the fiat obligation has been fixed, settlement proceeds through the card network’s clearing framework, where transaction data, issuer responsibilities, and merchant-acquirer claims are reconciled for final payment.

    In crypto-funded virtual card models, the prior asset liquidation does not alter standard network settlement processes; it simply changes the source of prefunded liquidity supporting issuer commitments.

    • Clearing files confirm amount, merchant category, interchange, and routing details.
    • The issuer remits funds to the network or designated settlement bank.
    • The acquirer receives net proceeds for merchant crediting after applicable fees.

    This architecture preserves transaction efficiency by separating blockchain conversion from downstream card obligations.

    The merchant is paid in fiat under familiar timelines, while the on-ramp absorbs crypto volatility, liquidity management, chargeback exposure, compliance controls, and any temporary funding mismatches internally.

    Network Choice and Downstream Program Structure

    Network choice affects acceptance footprint, program rules, and sometimes economics — though for most virtual card use cases, both networks serve well and provider capability matters more than network branding. Teams planning to distribute cards to their own clients should note that a virtual Visa card issuing platform API for resellers will define what program structures are available downstream, so network questions belong early in provider due diligence.

    Why Do On-Ramps Beat Manual Cash-Outs?

    Why do integrated on-ramps generally outperform manual cash-outs in the context of crypto-funded virtual cards? Their superiority lies in automation, speed, and operational certainty.

    Among the principal on-ramp advantages are real-time conversion, embedded compliance checks, and direct balance provisioning within the card environment. These features reduce user intervention, limit settlement delays, and lower the probability of transfer errors or abandoned transactions.

    How Do Crypto Cards Fit Payment Rails?

    How, then, do crypto-funded cards operate within conventional payment infrastructure? They typically sit atop an on-ramp stack that authorizes a card transaction, liquidates designated digital assets, and settles the merchant-facing payment in fiat.

    To the merchant acquirer and point-of-sale system, the transaction resembles a standard card purchase, while conversion and compliance occur behind the scenes. This architecture shapes user experience by reducing exposure to exchange mechanics at checkout.

    • Authorization occurs first, with balance verification and risk checks.
    • Asset conversion follows, translating crypto value into fiat funding.
    • Settlement completes through established card-processing workflows.

    Among the notable crypto card benefits are faster spending access, familiar acceptance patterns, and simplified treasury movement for individuals holding digital assets.

    Their role is therefore integrative, not disruptive, within existing retail payment rails today.

    Which Networks Support Crypto Card Payments?

    Support for crypto-funded virtual cards is concentrated within the major card networks, most notably Visa and Mastercard, which provide the underlying payment infrastructure.

    Their established merchant ecosystems determine where these products can be used in practice, linking crypto conversion to conventional card acceptance.

    As a result, global acceptance reach depends less on the digital asset itself than on the network footprint and issuer relationships behind the card.

    Major Card Networks

    Network compatibility determines whether a crypto-funded virtual card can function at ordinary online and point-of-sale checkouts. Most programs rely on established schemes such as Visa and Mastercard, while some issuers also integrate Discover or regional rails where technically feasible. Their role is not to handle cryptocurrency directly, but to authorize fiat-denominated card payments after the on-ramp converts assets at funding.

    Visa commonly appears in crypto card issuance because of broad issuer support and mature tokenization tools.

    Mastercard is similarly prominent, emphasizing authorization controls, settlement reliability, and transaction efficiency.

    Alternative networks matter where pricing, issuer access, or card network dynamics influence program design.

    Accordingly, network choice affects processing rules, token provisioning, chargeback procedures, compliance integration, and the operational flexibility available to crypto-backed card providers and issuers.

    Global Acceptance Reach

    Although crypto-funded virtual cards are linked to digital-asset balances at the funding layer, their practical acceptance depends on whether the issued credential rides on card networks with broad merchant coverage across e-commerce, mobile wallets, and in-store terminals.

    In practice, Visa and Mastercard currently provide the widest global adoption, reflecting deep merchant integration and strong support for digital commerce. Where these networks are available, transaction efficiency and user experience generally resemble conventional prepaid or debit products, which reinforces consumer trust.

    American Express and Discover may appear in selected programs, but acceptance breadth is narrower and often shaped by regional market demand. Consequently, network selection determines payment flexibility, especially for cross border transactions.

    This competitive landscape illustrates how fintech innovation still relies on incumbent rails to scale crypto spending beyond niche use cases globally.

    How Do On-Ramps Handle KYC and AML?

    How, then, do crypto on-ramps manage identity verification and financial crime controls when issuing or funding virtual cards? They apply KYC processes and AML compliance controls at onboarding and throughout account activity.

    User verification typically combines document checks, biometric matching, and database screening to support identity authentication under applicable regulatory frameworks. Customer due diligence and risk assessment determine access levels, funding limits, and enhanced review triggers.

    • Identity records are validated against sanctions, PEP, and adverse-media databases.
    • Transaction monitoring flags unusual funding patterns, velocity spikes, and wallet exposures.
    • Data protection controls govern storage, sharing, and retention of sensitive user information.

    Together, these measures support fraud prevention while preserving card-network integrity. On-ramps therefore function as compliance gateways, translating crypto activity into monitored, policy-aligned payment access across jurisdictions and counterparties.

    What Fees Shape Crypto Card Costs?

    Costs associated with crypto-funded virtual cards are shaped by a layered fee structure spanning asset conversion, account servicing, and payment execution. Providers typically apply conversion fees when digital assets are sold into fiat, with effective pricing influenced by quoted exchange rates and internal spreads.

    Additional transaction fees may arise from blockchain settlement, especially during periods of network congestion that elevate network fees.

    Beyond conversion, users may encounter recurring service charges tied to wallet maintenance, inactivity, or premium account tiers. Some programs also assess fees for card issuance, replacement, or expedited provisioning.

    Cross-border usage can trigger a foreign transaction surcharge, adding another variable to final cost. Careful scrutiny is therefore required, because advertised pricing may exclude hidden costs embedded in spreads, minimums, or merchant-side processing arrangements and settlement timing assumptions.

    Why Are Stablecoins Ideal for Crypto Cards?

    Why do stablecoins fit crypto-funded card programs so effectively? Their core appeal lies in reducing exchange-rate uncertainty between wallet funding and card spending. Unlike volatile cryptocurrencies, stablecoins support predictable balances, clearer user expectations, and more consistent authorization outcomes at the point of purchase.

    • Price stability helps preserve purchasing power between deposit and transaction.
    • Stablecoin advantages include simpler budgeting, clearer displayed values, and reduced slippage exposure.
    • They can improve operational consistency for card platforms managing prefunded balances.

    For virtual card programs, these characteristics matter because card usage depends on immediacy and trust. A user expecting $100 in available value cannot reliably transact if market swings erase spendable funds within minutes.

    Stablecoins therefore align digital asset funding with card-network norms centered on stable denominations, transparent value, and dependable consumer experience.

    How Do On-Ramps Settle With Issuers?

    In practice, on-ramps settle with issuers by converting user-funded crypto balances into fiat or fiat-equivalent settlement value and transmitting those funds through the banking and card-processing rails that support the card program. This usually occurs after authorization, when the on-ramp calculates the final funded amount, applies fees or spreads, and delivers prefunded or same-cycle liquidity to the issuer or program manager.

    The precise settlement mechanics depend on network rules, processing timelines, custody structure, and treasury controls. Some providers maintain omnibus fiat accounts, while others rely on regulated banking partners or stablecoin redemption workflows before fiat payout.

    Issuer agreements define reserve requirements, reconciliation standards, chargeback funding responsibilities, and reporting obligations. Effective settlement design therefore depends on timing certainty, liquidity management, operational transparency, and strict alignment between crypto conversion processes and card-program obligations.

    Which Use Cases Fit Crypto-Funded Cards?

    Utility defines the strongest use cases for crypto-funded virtual cards. The most compelling use case examples center on everyday online spending, travel, subscriptions, and cross border payments, where transaction speed and card acceptance matter more than holding tokens directly.

    Consumer adoption rises when conversion is invisible, balances update instantly, and security features align with familiar card controls.

    • E-commerce checkout, where merchant benefits include broader payment reach and fewer abandoned carts.
    • Remittances and travel spending, supporting financial inclusion for users with limited banking access.
    • Incentive programs, where loyalty rewards can be funded from digital assets and redeemed through standard merchants.

    These cards fit scenarios requiring practical spendability, predictable settlement, and low user friction. Their value proposition weakens when volatility, fees, or compliance frictions outweigh convenience.

    How Can Fintechs Launch Crypto Card Programs?

    Although product design often receives the most attention, fintechs typically launch crypto-funded card programs by sequencing regulatory approval, issuer and network partnerships, custody and conversion infrastructure, and transaction monitoring into a single operating model.

    Execution usually begins with jurisdictional scoping, licensing analysis, and sponsor-bank alignment, because compliance obligations differ across markets and customer segments. Firms then structure crypto partnerships for wallet custody, liquidity sourcing, and real-time asset liquidation at authorization or settlement.

    Card economics require negotiated interchange sharing, processor connectivity, fraud controls, and dispute workflows compatible with network rules. Onboarding must integrate KYC, sanctions screening, and blockchain analytics to reduce financial-crime exposure.

    Clear treasury policies are also needed to manage prefunding, volatility, and reconciliation. Finally, user incentives should reflect sustainable unit economics rather than subsidized growth or excessive reward liabilities.

    Where Are Crypto-Funded Virtual Cards Heading?

    Future direction appears to center on three variables: rising stablecoin-funded spending, clearer regulatory frameworks, and more intelligent card integrations.

    Stablecoins are increasingly positioned as the settlement layer that can reduce volatility at the point of payment, while regulatory developments will determine how broadly issuers and fintechs can scale these programs.

    At the same time, smarter integrations across wallets, compliance systems, and card infrastructure are likely to shape usability, control, and adoption.

    Stablecoin Spending Growth

    Momentum is increasingly concentrated around stablecoin-denominated spending, as virtual card programs use dollar-pegged assets to reduce volatility at the point of payment while preserving the settlement advantages of crypto rails.

    This shift reflects practical demand rather than speculation, with stablecoin adoption accelerating where users prioritize predictability, liquidity, and faster fund access across merchants and platforms.

    For issuers, digital asset integration becomes easier when balances remain price-stable and conversion requirements are simplified.

    • Merchant acceptance improves when card-funded transactions resemble familiar fiat purchasing behavior.
    • Treasury management benefits from reduced exposure to intraday swings common in non-pegged crypto assets.
    • Cross-border use cases expand as settlement speed and transferability support global card activity.

    As infrastructure matures, stablecoin spending appears positioned to become the default bridge between crypto balances and everyday card utility worldwide.

    Regulatory Paths Ahead

    As stablecoin-linked card activity scales, regulatory direction is likely to determine which crypto-funded virtual card models achieve broad distribution and institutional support.

    Jurisdictions are expected to refine legal frameworks governing issuance, custody, settlement, and disclosure, with regulatory compliance becoming a primary differentiator among providers.

    Future adoption will likely favor programs aligned with consumer protection standards, licensing requirements, and stronger financial oversight.

    Firms operating across borders may face added complexity as international regulations diverge on reserve treatment, transaction monitoring, and permissible wallet structures.

    In that environment, digital asset policies will increasingly shape partner selection, product design, and underwriting criteria.

    Providers that embed rigorous risk management, anti-fraud measures, and transparent reporting are better positioned to satisfy supervisors, reduce enforcement exposure, and support broader market stability over time.

    Smarter Card Integrations

    Smarter card integrations are likely to center on tighter connections between wallets, card processors, banking rails, and merchant systems, reducing friction across authorization, funding, and settlement.

    • Digital wallets may automate prefunding and balance checks through smart contracts.
    • Better technology integration can improve transaction speed, routing efficiency, and reporting.
    • Embedded security measures may strengthen user privacy while easing compliance demands.

    Current market trends indicate that issuers will differentiate through user experience, merchant acceptance, and interoperability.

    The competitive landscape increasingly favors platforms that connect crypto liquidity to conventional payment infrastructure without exposing users to operational complexity.

    However, adoption barriers remain substantial, including fragmented standards, uneven regional support, and residual trust concerns.

    Smarter integrations therefore appear less cosmetic than structural, reshaping how crypto-funded virtual cards function at scale globally.

    Frequently Asked Questions

    Can Crypto-Funded Virtual Cards Build Credit History?

    Generally, they cannot build credit history unless issuers report activity to bureaus. Credit scoring depends on reported repayment behavior; blockchain integration, spending limits, and digital identity features may support underwriting, but usually not traditional credit-file creation.

    Are Crypto-Funded Cards Usable for Recurring Subscription Billing?

    Yes; like a clock fed by shifting tides, they can support recurring subscriptions when issuers permit merchant continuity. Their subscription flexibility depends on card stability, authorization rules, and payment processing compatibility with merchants’ rebilling systems.

    What Dispute Rights Apply to Crypto-Funded Virtual Card Purchases?

    Dispute rights generally follow the card network and issuer terms, not blockchain rules, covering unauthorized charges, billing errors, and merchant disputes. Outcomes depend on transaction verification, cardholder protections, issuer policies, and formal dispute resolution procedures.

    Can Employers Issue Crypto-Funded Virtual Cards for Payroll?

    Yes, employers can issue crypto-funded virtual cards for payroll; like a runner passing batons, pilots showed wallet integration sped access, but tax implications, employee acceptance, and security concerns determine legality, usability, and prudent deployment across jurisdictions.

    How Do Refunds Work on Expired Crypto-Funded Virtual Cards?

    Refunds on expired crypto-funded virtual cards are typically permitted through issuer-led refund processing, provided the underlying account remains active. Card expiration usually blocks new purchases, not returned funds, which are credited to the associated wallet or settlement account.

    Final words

    Crypto-funded virtual cards illustrate how digital assets can move beyond speculation and into routine commerce. By linking wallets to regulated on-ramps, by converting balances into spendable fiat, by coordinating authorization, settlement, and compliance, these systems reduce friction between crypto markets and card networks. Their significance lies not only in convenience, but in connection; not only in access, but in acceptance; not only in spending, but in strengthening the infrastructure that supports broader everyday use of digital value.

  • How Card29 Supports Digital Agencies in Israel

    How Card29 Supports Digital Agencies in Israel

    You’ll streamline billing, cut DSO, and protect margins by using Card29’s multi-currency invoicing, automated collections, and subscription billing that syncs with Xero, QuickBooks, HubSpot and Asana. Assign budgets, auto-generate milestone invoices, and track payments in real time to reclaim billable hours and improve cash flow. Flat, transparent fees keep profitability predictable, while local support ensures VAT and payroll compliance in Israel. Keep going to see implementation steps, pricing, and proven agency outcomes.

    Key Takeaways

    • Centralized billing and tokenized payments streamline agency-client invoicing, approvals, and real-time audit trails.
    • Multi-currency invoicing with automated exchange rates and flat transparent fees reduces payment friction and boosts margins.
    • Subscription billing automation and smart dunning shorten invoice-to-cash cycles and recover failed payments.
    • Prebuilt integrations (Xero, QuickBooks, HubSpot, Asana) sync billing, CRM, and project triggers for accurate reconciliations.
    • Local Israeli support ensures VAT compliance, payroll guidance, and tailored accounting workflows for regulatory alignment.

    Why Card29 Is the Better Agency Payments Solution

    Choose Card29 and you’ll simplify agency payments without sacrificing control or visibility. You’ll streamline workflows so agency collaboration becomes effortless: assign budgets, approve spend, and track invoices in one shared dashboard that keeps teams aligned and accountable.

    You’ll reduce reconciliation time and free resources to focus on client growth.

    You’ll also strengthen payment security with tokenization, role-based access, and real-time audit trails, so sensitive data stays protected while approvals stay fast.

    You’ll integrate Card29 into existing accounting tools, preserving operational continuity and delivering measurable ROI through faster cash flow and fewer billing errors.

    You’ll gain a partner that prioritizes transparent controls, predictable outcomes, and collaborative processes that scale with your agency’s ambitions.

    The Card That Beat Our Coffee to the Table

    We didn’t think “getting a card” and “instant” belonged in the same sentence until a friend proved otherwise. He spins up an instant virtual card whenever he needs one on the spot. He recommended Card29, and the speed genuinely surprised us. No mailbox, no week-long wait, no risking our primary credit card in the meantime—just a ready-to-use prepaid card in seconds. When you need to pay right now, a VCC turning up that fast is the entire point.

    Multi‑Currency Invoicing With Card29 for International Clients

    You’ll streamline billing for international clients by offering multi-currency invoices that match each client’s preference and local regulations.

    Card29 handles automated exchange-rate calculations and applies consistent, transparent rates so you don’t waste time on manual conversions.

    Together we’ll reduce payment friction and speed up cash flow with accurate, predictable cross-border billing.

    Multi‑Currency Billing Options

    Offering multi-currency invoicing with Card29 lets you bill international clients in their preferred currency, reducing friction and improving conversion rates. You’ll present clear line items and totals in client-facing currencies so they immediately understand costs; that transparency highlights multi-currency advantages and strengthens trust.

    Card29’s billing options let you set per-client billing currency, recurring invoice currencies, and consolidate reports by currency for simpler reconciliation. You can collaborate with clients on contract terms knowing billing won’t create surprises, and your finance team can prioritize settlements that maximize cash flow.

    These features boost global competitiveness by making your services easier to buy across markets. Implementing them strategically helps you win more international projects and accelerate revenue.

    Automated Exchange Rate Handling

    Once you’ve set client billing currencies, Card29 automates exchange rate management so invoicing stays accurate and predictable across borders.

    You’ll reduce manual conversions and errors because rates update automatically and integrate into invoice totals, giving clients clear, timely charges.

    Collaborate with your finance team to set preferred rate sources and tolerance thresholds, so you control when to lock rates versus use live market feeds.

    Card29’s automated reporting surfaces the impact of currency fluctuations on margins and cash flow, letting you make strategic pricing or hedging decisions fast.

    You’ll deliver consistent billing experiences to international clients, preserve profitability, and scale cross-border services without adding administrative overhead or exposing the agency to avoidable FX risk.

    Cut DSO and Accelerate Agency Cash Flow

    You can shorten invoice-to-cash cycles by automating payment options and streamlining invoice delivery so clients pay sooner.

    With real-time payment visibility you’ll spot delays immediately and prioritize follow-ups that move cash faster.

    Automated collection triggers keep tasks consistent and reduce manual chase, so your agency improves liquidity without adding overhead.

    Faster Invoice-to-Cash

    Speed up your invoice-to-cash cycle to cut DSO and keep your agency’s cash flow predictable and ready for growth.

    You’ll streamline billing with invoice automation that reduces errors and shrinks approval time, so clients get clear, accurate invoices faster.

    Card29 helps you standardize templates, trigger reminders, and manage approvals collaboratively, reducing disputes and late payments.

    You’ll pair automated invoicing with efficient cash reconciliation to close books faster and spot gaps between expected and received funds.

    That clarity lets you prioritize collections, optimize working capital, and fund strategic hires or campaigns without waiting on payments.

    Together we’ll set measurable targets, monitor progress, and iterate processes so your agency confidently converts revenue into actionable cash.

    Real-Time Payment Visibility

    While invoices and bank statements still roll in, real-time payment visibility lets your agency act the moment cash movements occur—reducing DSO and keeping campaigns, hires, and vendor commitments from stalling.

    You’ll get payment tracking and visibility insights that turn lag into leverage, so you can prioritize spend, reallocate resources, and forecast with confidence. This isn’t about alerts alone; it’s about giving teams a shared operational picture to make faster, aligned decisions.

    1. See incoming payments by client and campaign in real time.
    2. Reconcile cash flows faster to close books and free working capital.
    3. Identify shortfalls early and reassign budget to high-impact work.
    4. Share visibility insights across finance and account teams for coordinated action.

    Real-time data translates into measurable cash acceleration.

    Automated Collection Triggers

    Real-time visibility helps you spot cash as it moves; automated collection triggers make sure those insights turn into action.

    You’ll define trigger events tied to invoice milestones—due dates, partial payments, or contract expirations—and Card29 will fire automated notifications to clients and internal teams. That reduces manual follow-up, cuts days sales outstanding, and protects margins without adding headcount.

    You’ll collaborate with Card29 to tailor timing, tone, and escalation paths so outreach feels consistent and professional.

    Reporting shows which triggers work and where clients stall, letting you optimize workflows and collections strategy. The result: steadier cash flow, predictable forecasting, and more time for growth-focused work instead of chasing payments.

    Automate Subscriptions and Recurring Billing With Card29

    Automating subscriptions and recurring billing with Card29 lets you eliminate manual invoicing, reduce churn, and free your team to focus on growth initiatives.

    You’ll use subscription management and billing automation to create predictable revenue streams, personalize plans, and recover failed payments with smart dunning. Card29 integrates with your CRM and billing stack so you can scale without adding headcount.

    1. Centralize plans, trials, and upgrades.
    2. Automate invoices, receipts, and proration.
    3. Retry failed charges and trigger alerts.
    4. Report MRR, churn, and cohort trends.

    You’ll collaborate with Card29 to configure workflows that match client lifecycles, run experiments on pricing and retention, and measure outcomes.

    The result: steadier cash flow and more time for strategic growth.

    Transparent Fees That Protect Agency Margins

    You need fee clarity to protect your margins, and Card29 gives you flat, predictable processing rates so you can price services confidently.

    With no hidden markup fees, you’ll avoid surprise costs that erode profitability.

    Let’s map how transparent pricing keeps your agency’s revenue predictable and scalable.

    Flat, Predictable Processing Rates

    When margins matter, Card29 gives your agency flat, predictable processing rates so you can price projects confidently and protect profitability.

    You’ll get a flat rate structure that removes guesswork and lets you forecast predictable costs across clients and campaigns. That clarity helps you negotiate retainers, set clear KPIs, and scale without surprise expenses.

    1. Simple flat rate per transaction for consistent margin planning.
    2. Predictable costs across payment methods to avoid variability.
    3. Clear reporting so your team tracks processing spend in real time.
    4. Scalable pricing that supports growth without hidden surprises.

    You’ll work collaboratively with Card29 to align pricing to your business model, drive predictable outcomes, and preserve agency margins.

    No Hidden Markup Fees

    Because transparency matters to your bottom line, Card29 charges straightforward fees with no hidden markups so you can protect agency margins and price confidently.

    You’ll see transparent pricing that aligns with project bids, letting you forecast revenue and keep proposals competitive. When you evaluate campaigns, Card29’s clarity removes surprises—no hidden fees will erode negotiated rates or client trust.

    That predictability simplifies budgeting, informs client conversations, and speeds approval cycles. You’ll collaborate with Account Managers who review fee structures and suggest margin-preserving options tailored to your service mix.

    The result: cleaner P&L statements, steadier margins, and fewer disputes over billing. Card29’s approach makes pricing a strategic advantage, not an accounting headache.

    Retainer and Project Billing Workflows Made Simple

    While managing mixed retainer and project work can feel chaotic, Card29 lets you standardize billing so teams stay aligned and cash flow stays predictable.

    You’ll set clear retainer agreements, map deliverables, and link them to your project management milestones so invoices mirror real progress. That reduces disputes and speeds approvals.

    You’ll benefit from a simple, repeatable workflow that scales across clients and teams:

    1. Define retainer terms and scope per client.
    2. Break projects into billable milestones.
    3. Auto-generate invoices tied to milestone completion.
    4. Track payments and adjust forecasts in real time.

    This approach keeps account managers, finance, and delivery teams collaborating efficiently, so you hit deadlines, preserve margins, and improve client satisfaction.

    Integrations: Xero, QuickBooks, HubSpot, Asana and More

    Linking your billing workflow to the tools your teams already use keeps those streamlined retainer-to-invoice processes running smoothly.

    You’ll gain Xero integration benefits like automated reconciliations and clearer financial reporting, and QuickBooks compatibility features let your accounting stay synchronized without manual exports.

    HubSpot automation advantages accelerate client lifecycle touches, so your sales and billing teams act in unison.

    Integrating Asana project management aligns tasks with billing triggers, reducing scope creep and missed invoices.

    These connections drive payment processing efficiency by shortening time-to-pay and cutting errors.

    You’ll also see client onboarding improvements through pre-populated contracts and automated billing schedules, enabling your agency to scale delivery while keeping finance, sales, and project teams tightly coordinated for measurable results.

    Local Support, Tax Compliance, and Israeli Regulatory Coverage

    As you scale in Israel, Card29 pairs local support with built‑in tax compliance so your agency stays accurate and audit-ready without adding overhead.

    You’ll access local partnerships and support services that understand VAT rules, payroll nuances, and frequent regulatory updates.

    Card29 helps you face compliance challenges proactively, reducing manual reconciliation and risk.

    1. Streamlined VAT reporting synced to local rules
    2. Real-time alerts for regulatory updates impacting billing
    3. Integrated workflows with local accountants and partners
    4. Support services that guide audits and documentation

    You’ll collaborate with specialists who translate regulations into operational steps, freeing you to focus on growth.

    The result: predictable compliance, faster financial close, and fewer surprises during inspections.

    Real Agency Case Studies: Savings, Time Reclaimed, Growth

    Because you want measurable results, Card29 worked with real Israeli agencies to cut costs, reclaim billable hours, and unlock new client capacity—delivering concrete savings, streamlined operations, and faster growth trajectories.

    You’ll see case study insights showing reduced processing costs by up to 18% and reclaimed time equivalent to multiple weekly billable days per account manager.

    Working together, you’ll adopt targeted workflow changes, automated payment reconciliations, and consolidated vendor billing that translate into clear efficiency metrics and predictable monthly savings.

    Those outcomes let you pitch expanded services, shorten onboarding, and scale without proportional headcount increases.

    Card29 partners with you to quantify gains, set milestones, and iterate quickly so your growth is driven by verifiable improvements, not assumptions.

    Implementation Checklist, Pricing Tiers, and ROI Calculator

    While you’re adopting the workflow changes from our case studies, use this implementation checklist to map responsibilities, timelines, and quick wins so you see ROI fast. The checklist pairs with clear pricing tiers and a built-in ROI calculator that projects savings by account, month, and year.

    You’ll follow proven implementation strategies that make onboarding predictable, assign owner-level tasks, and track milestone KPIs. Use pricing comparisons to choose the tier that matches client volume and expected automation gains. The ROI calculator turns those inputs into net savings and payback period so you can sell confidently.

    1. Define roles and 30/60/90 day milestones
    2. Select tier via pricing comparisons
    3. Run ROI scenarios per client
    4. Execute quick-win automations

    Final words

    You’re not just switching payments — you’re arming your agency with a partner that thinks like you do: strategic, collaborative, and relentlessly results-driven. Like a seasoned navigator guiding a ship through changing tides, Card29 steadies cash flow, simplifies compliance, and automates billing so you reclaim time to win clients and scale. Choose the solution that protects margins, builds predictable revenue, and turns operational friction into forward motion.

  • Virtual Cards for Paying SaaS and CRM Tools in Colombia

    Virtual Cards for Paying SaaS and CRM Tools in Colombia

    You should use vendor‑specific virtual cards to pay SaaS and CRM tools in Colombia because they cut fraud, enforce per‑subscription limits and expiries, and give transaction‑level metadata that streamlines reconciliation and VAT tracking. They lower chargebacks and automate card rotation for trials, though you’ll weigh issuer fees, token lifecycle risks and local invoicing rules. Implement pilot controls, monitor auth success and set alerts for expiries — continue for practical provider selection, rollout steps and pitfalls to avoid.

    Key Takeaways

    • Use vendor-specific virtual cards with per-subscription limits and expiries to prevent unauthorized recurring SaaS and CRM charges.
    • Leverage real-time transaction feeds and metadata to simplify reconciliation and attribute costs to projects and teams.
    • Implement tokenization and automated card rotation to reduce fraud and failed authorizations for CRM integrations.
    • Configure spend controls (MCC rules, rolling limits, declines) based on historical SaaS spend to avoid overages.
    • Ensure local compliance: maintain DIAN-ready invoices, VAT tagging, and daily bank-feed reconciliation for audits.

    Should Colombian Companies Use Virtual Cards for SaaS?

    Should Colombian companies use virtual cards for SaaS? You should consider them if you value control, cost visibility, and reduced fraud exposure.

    Data shows virtual card benefits include per-vendor limits, single-use numbers, and easier reconciliation—reducing chargeback and unauthorized recurring charges by measurable margins.

    You’ll improve subscription management through automated card rotation, merchant-level budgeting, and clearer audit trails, which cut manual invoice handling time.

    Risks remain: currency conversion fees, platform lock-in, and gaps with vendors that reject virtual cards.

    Mitigate by testing with low-value subscriptions, tracking FX impact, and keeping backup payment methods.

    If you prioritize operational efficiency and risk reduction, virtual cards are a pragmatic option; quantify savings before full rollout.

    How Virtual Cards Work for Subscriptions and Trials

    When you sign up for a SaaS trial or subscription with a virtual card, the provider issues a unique card number (single-use or merchant-restricted), an expiration, and a CVV tied to a controlled funding source—so you can set per-vendor limits, lifespans, and transaction rules that minimize exposure to unexpected charges.

    You’ll assign budgets and validity windows, auto-disable cards after trials, and enforce MCC or merchant restrictions to reduce fraud and runaway renewals.

    Real-time transaction feeds let you reconcile costs, detect anomalies, and attribute spend to teams or projects for clearer subscription management. Metrics like failed-charge rates, renewal dates, and lifetime spend per vendor become actionable.

    These virtual card benefits lower payment risk, simplify audits, and make trial-to-paid conversions measurable and controllable.

    Settling Foreign Invoices Without the Hassle

    Paying suppliers and tools across borders used to mean fees, flags, and the odd declined charge. A friend who imports goods smooths it all with a virtual card for paying international vendors. He pointed us to Card29, and our cross-border spending got noticeably easier. Each overseas vendor draws on a funded prepaid card with a clear limit, sidestepping the surprises of running everything through one credit card. For anyone dealing internationally, a purpose-built VCC strips out a lot of quiet friction.

    Virtual Cards vs Company Debit/Credit Cards: A Decision Framework

    When you compare virtual cards to company debit/credit cards, focus on measurable gains: virtual cards let you enforce per-subscription spend limits and reduce fraud exposure by isolating vendor credentials.

    You’ll cut reconciliation time with transaction-level metadata and automated reporting, lowering accounting errors and audit risk.

    Balance those benefits against issuer fees and integration costs to decide which yields the best net risk-adjusted return for your SaaS and CRM stack.

    Cost Control Advantages

    Compare spend signals and control levers across virtual cards and company debit/credit cards to decide which minimizes cost leakage for your SaaS and CRM stack.

    You’ll see virtual cards improve cost efficiency by enabling per-subscription limits, preset expiration dates, and merchant whitelisting, so unauthorized renewals and duplicate services drop.

    Use virtual-card telemetry to tag expenses in real time, simplifying budget management and accelerating variance analysis against forecasts.

    Traditional cards centralize payments but blur granular accountability, increasing reconciliation time and error rates—studies show manual reconciliation can consume 5–10% of finance capacity.

    Choose virtual cards when you need tight spend granularity, automated tagging, and lower operational overhead; keep company cards only for legacy vendors or low-volume scenarios where card issuance overhead outweighs control benefits.

    Security And Fraud Prevention

    Although virtual cards reduce several common fraud vectors, you should evaluate both options against your threat model and operational needs.

    Virtual cards limit exposure with single-use numbers and strict spend caps; company debit/credit cards offer broader vendor relationships but greater theft risk.

    Prioritize data encryption for token storage and enforce real-time transaction alerts to detect anomalies.

    1. Implement tokenization and end-to-end data encryption for stored credentials; measure breach surface reduction.
    2. Use transaction alerts with threshold-based and anomaly-detection rules; aim for sub-minute detection and automated lockouts.
    3. Maintain role-based issuance, periodic credential rotation, and least-privilege limits; quantify residual risk and incident response time.

    Choose the solution that minimizes measurable fraud probability while fitting your workflow and vendor requirements.

    Accounting And Reconciliation

    Reconciliation precision drives your choice between virtual cards and company debit/credit cards: virtual cards simplify vendor-level matching with single-use numbers and built-in metadata, while traditional cards consolidate statements but often require manual line-item allocation and chargeback handling.

    You’ll find virtual card benefits include automated mapping to invoices, immediate reconciliation flags, and per-subscription limits that reduce disputed charges.

    With company debit/credit cards, you get consolidated monthly visibility but increased bookkeeping overhead: you’ll need to parse bulk statements, attribute costs, and manage refunds manually.

    For robust expense tracking, adopt a hybrid policy—use virtual cards for SaaS/CRM vendors and retain a corporate card for bank fees or unpredictable expenses.

    Measure time-to-reconcile, error rates, and fraud incidents to guide policy.

    Local Payment Rails and Multi‑Currency Options in Colombia

    When you integrate virtual cards for SaaS and CRM payments in Colombia, prioritize local payment rails like ACH-equivalents (PSE) and tarjeta débito networks to reduce FX friction and settlement delays.

    You’ll need to map local payment infrastructure against multi currency challenges, fintech partnerships, and digital wallet integration to minimize fees and compliance risks.

    Focus on transaction speed optimization and clear reporting to limit payment reconciliation hurdles under a changing regulatory landscape impact.

    1. Evaluate merchant acceptance rates and routing to local rails to avoid costly FX conversions.
    2. Partner with fintechs offering on‑shore settlements and multi‑currency pools to manage currency exposure.
    3. Implement reconciliation tools that tag rails, wallets, and FX events for auditability and faster dispute resolution.

    Which SaaS and CRM Vendors Accept Virtual Cards in Colombia?

    After mapping local rails and multi‑currency flows, you’ll want to identify which SaaS and CRM vendors in Colombia actually accept virtual cards so you can route payments to avoid FX hits and settlement delays.

    Start by cataloging vendor partnerships and their payment flexibility: global platforms like HubSpot, Salesforce, and Atlassian often accept virtual cards, while local providers vary.

    Evaluate subscription management APIs and integration capabilities to automate renewals and reduce manual errors.

    Quantify cost efficiency by comparing currency conversion fees and transaction transparency per vendor.

    Assess compliance challenges—local tax and AML rules—and how they affect user experience.

    Prioritize vendors that support payment automation, clear reporting, and seamless integration to minimize operational risk and control spend.

    Creating Vendor‑Specific Cards to Control Department Budgets

    Assign vendor-locked virtual cards so you can cap spend per supplier and prevent cross-vendor charge leakage.

    Use departmental spend controls to set monthly limits, transaction caps, and real-time alerts; companies that implement these controls typically reduce budget overruns by 20–35%.

    Monitor authorization logs and reconcile variances weekly to mitigate fraud and compliance risk.

    Vendor‑Locked Card Limits

    If you need tight control over departmental SaaS spend, create vendor‑locked cards that only work with specified merchants and set per‑vendor limits tied to budget lines. You’ll reduce fraud surface and enforce vendor loyalty while preserving card usability for approved purchases.

    Use transaction data to define limits, and tie thresholds to forecasting models.

    1. Configure limits per vendor based on historical spend and expected growth; this cuts unexpected overages by measurable percentages.
    2. Set realtime declines for out‑of‑scope merchants and soft alerts when usage nears limits; this balances control with operational continuity.
    3. Apply rolling windows and auto‑adjust rules for seasonal vendors to avoid unnecessary refusals while maintaining strict cost discipline.

    Monitor exceptions, report variance, and iterate controls monthly to minimize risk.

    Departmental Spend Controls

    When you create vendor‑specific virtual cards for each department, you enforce budget boundaries at the point of purchase and cut reconciling time by up to 40%.

    You’ll assign cards with precise budget allocation, automated approval workflows, and preset limits so teams can spend without breaching monthly caps.

    Departmental accountability improves because each charge ties to a card owner and project code, enabling real‑time expense tracking and spending transparency across SaaS and CRM vendors.

    That setup empowers teams to move faster while central controllers retain financial oversight and reduce invoice backlog.

    Risk falls with integrated compliance monitoring, flagging anomalies and policy breaches instantly.

    Implement this to balance team empowerment with strict controls and measurable cost discipline.

    Set Limits and Expiries to Control Recurring Subscriptions

    Because recurring charges can quietly compound into unexpected spend, you should set hard limits and expiries on virtual cards to control SaaS and CRM subscriptions.

    Use spending limits and subscription expiries to enforce budget oversight and financial discipline, preserving cash flow and enabling precise expense tracking.

    Limits aid vendor management by capping monthly and per-transaction exposure; expiries force renewal decisions and reduce orphaned subscriptions.

    This drives operational efficiency and risk mitigation while keeping payment flexibility for approved vendors.

    1. Define monthly and per-charge spending limits linked to budget lines to improve cash flow forecasting.
    2. Apply automatic subscription expiries timed to contract review cycles for vendor management and expense tracking.
    3. Monitor limit breaches and expiry alerts for rapid budget oversight and corrective action.

    Handling Recurring Charges, Tokenization, and Card Updates

    Though virtual cards simplify vendor payments, you must manage recurring charges, tokenization, and card updates proactively to prevent failed transactions and billing drift.

    You should map each subscription to a single virtual PAN or token and record tokenization metadata to detect mismatches. Implement token management strategies that include token refresh schedules, secure storage, and automated alerts when tokens or underlying cards expire or are replaced.

    Monitor authorization success rates and set thresholds (e.g., >98% success) to trigger remediation workflows. Integrate subscription lifecycle management with your finance and procurement systems so renewals, cancellations, and limit changes update card status in real time.

    Regularly audit failed charge reasons, quantify failure impact on spend, and enforce SLA-driven remediation to reduce revenue leakage.

    Automate Reconciliation With Virtual Card Metadata

    If you tie virtual card metadata—PAN/token IDs, merchant category, transaction timestamps, and spending controls—directly into your reconciliation engine, you’ll cut manual match time by orders of magnitude and surface anomalies within hours instead of days.

    You’ll implement metadata integration and automated tracking so each charge maps to a purchase order, subscription ID, and cost center automatically. That reduces allocation errors and speeds month-end close.

    1. Use PAN/token linkage to match gateway records to ledger entries, lowering false positives and improving audit trails.
    2. Capture merchant category and timestamps to flag out-of-policy spend and reconcile timing variances.
    3. Leverage spending-control logs for post-event verification and trend analysis, enabling rapid risk remediation and tighter controls.

    Managing Refunds, Disputes, and Chargebacks in Colombia

    When a customer disputes a charge in Colombia, you’ll face a regulated chargeback process that can take 30–90 days depending on the card network and issuer.

    Track refund timelines closely—local banks often require specific documentation within strict windows, and delays increase your financial and reputational risk.

    Use card-level metadata and automated workflows to prove legitimate transactions and shorten resolution time.

    Local Chargeback Process

    Because Colombian banks and card networks have specific timelines and evidence requirements, you need a clear, documented local chargeback workflow to manage refunds, disputes, and chargebacks efficiently.

    You’ll track chargeback timelines, collect transaction logs, and standardize evidence (IP, invoices, consent records) to support dispute resolution. Train staff on escalation thresholds and regulatory notice windows to reduce financial and reputational risk.

    1. Map timelines: record issuer, scheme, and bank deadlines; automate alerts for each case.
    2. Evidence pack: assemble transaction metadata, communication logs, and service delivery proof to meet local evidentiary standards.
    3. Escalation & analytics: route high-value disputes to a specialist, log outcomes, and calculate win-rate and cost-per-dispute for continuous improvement.

    Refund Timelines Colombia

    Having a local chargeback workflow sets the stage for handling refund timelines specific to Colombia’s banks and card schemes. You’ll map expected windows: issuer-side chargebacks often resolve in 30–120 days, while merchant-initiated refund processing usually completes within 5–15 business days depending on the acquirer and card network.

    Track metrics: median refund processing time, dispute escalation rate, and time-to-resolution to spot bottlenecks. Align your refund policies with local regulations (SIC guidance) and card scheme rules to reduce reversals and fines.

    Maintain clear evidence trails—transaction logs, service records, and customer communications—to shorten dispute cycles. Automate notifications and reconciliation so you can act within statutory limits, mitigate fraud risk, and preserve merchant relationships through predictable, auditable refund timelines.

    Tax and Compliance Considerations for Colombian Businesses

    Although virtual cards simplify vendor payments and expense tracking, Colombian businesses must navigate specific tax and regulatory rules to avoid penalties.

    You’ll assess tax implications of SaaS spend, ensure compliance requirements align with invoicing standards, and maintain documentation practices that support tax deductions.

    Focus on reporting obligations for VAT and income tax, especially for international transactions and cross-border payment processing.

    1. Map regulatory guidelines and audit considerations: keep receipts, contract copies, and digital trails to prove financial transparency and support audits.
    2. Implement risk assessment tied to foreign currency fees, withholding tax, and service classification for correct tax treatment.
    3. Standardize invoicing standards and reporting cadence to meet DIAN requirements and internal control expectations.

    Accounting Best Practices for Virtual Card Transactions

    When you integrate virtual card transactions into your accounting workflow, implement consistent coding, real-time reconciliation, and clear approval trails to reduce errors and exposure to fraud.

    You should enforce transaction categorization rules tied to GL accounts so reports reflect SaaS and CRM spend accurately; aim for <24-hour reconciliation to catch mismatches.

    Use automated expense tracking that tags vendor, project, and subscription periods to support accruals and VAT documentation.

    Require pre-approval limits per card and monthly sampling to validate compliance; measure exceptions as a percentage of transactions and target <2% unresolved.

    Reconcile bank feeds to your ledger daily, and keep retention of receipts in a searchable format for audits.

    Review policies quarterly and adjust coding to reflect product or contract changes.

    Security Benefits and Common Fraud Risks for Virtual Cards

    You’ll cut exposure risk by issuing single-use or vendor-specific numbers that limit how much information attackers can steal.

    You can enforce transaction controls—limits, MCC restrictions, and expiration windows—to reduce unauthorized spend in real time.

    Combine those controls with anomaly and fraud-detection signals (unusual amounts, geolocation mismatches, repeated declines) to spot and stop attacks faster.

    Reduced Exposure Risk

    Because virtual cards tie single-use or merchant-specific numbers to defined limits and lifespans, they cut your exposure to stolen credentials and recurring fraud.

    You get clear risk management strategies and exposure mitigation techniques: tokenization reduces clear-text storage, ephemeral numbers limit replay attacks, and scoped credentials prevent lateral use. Data shows merchant-specific tokens drop successful fraud attempts by a material percentage versus static cards.

    1. Limit surface area: single-use or vendor-bound numbers reduce exposure windows and credential reusability.
    2. Reduce fraud escalation: time-bound cards halt recurring charges quickly, lowering loss magnitude.
    3. Simplify response: replacing or revoking a virtual card is faster than reissuing a physical card, speeding containment and forensic analysis.

    Transaction Controls

    Reduced exposure through scoped, time-bound numbers sets the groundwork for granular transaction controls that enforce how, where, and when funds move.

    You’ll apply transaction limits and card customization to match vendor relationships and subscription tiers, reducing unauthorized charges.

    Integrate approval workflows so purchases require sign-off, strengthening expense management and compliance monitoring.

    Use usage analytics and spending patterns to flag anomalies and refine budget tracking; these metrics let you reallocate limits and detect risky behavior early.

    Fraud alerts should trigger immediate card suspension and review, minimizing loss.

    Combine controls with clear vendor policies to limit stored credentials and recurring-payment abuse.

    Fraud Detection Signals

    When virtual card activity deviates from established patterns, your systems can detect early indicators of fraud—unusual merchant categories, spikes in transaction velocity, mismatched geolocations, and attempts to reuse single-use numbers are strong signals to flag.

    You’ll rely on automated fraud detection and continuous signal analysis to prioritize alerts and block risky flows before losses escalate. Combine behavioral baselines with rule-based thresholds and machine learning scores to reduce false positives and quantify risk exposure.

    1. Monitor velocity and spend anomalies to catch rapid, small-value tests that precede larger fraud.
    2. Correlate geolocation, device fingerprint, and merchant type to identify credential-stuffing or account-takeover attempts.
    3. Track token reuse and authorization declines to detect compromised provisioning or fraud rings.

    How to Pick a Colombian Virtual Card Provider for SaaS

    Which metrics matter most when choosing a Colombian virtual card provider for SaaS? Focus on measurable virtual card features: transaction limits, tokenization standards (PCI DSS/EMV), real-time spend controls, FX margins, and settlement times.

    Compare providers by uptime SLAs, dispute resolution speed, and historical fraud rates. You’ll weigh integration APIs, webhook reliability, and existing connector support for major SaaS/CRM platforms.

    Quantify cost: per-card fees, authorization declines, and chargeback percentages to model annualized expense and risk exposure. Verify legal compliance—local AML/KYC and data residency—and vendor insurance or indemnity limits.

    Run provider comparisons with a scorecard (security, cost, integration, support, compliance). Prioritize vendors that minimize operational friction while capping fraud and reconciliation risk.

    Implementation Checklist for Rolling Out Virtual Cards

    Because rolling out virtual cards touches finance, security, and ops, you should follow a compact, measurable checklist that reduces friction and caps risk.

    You’ll align stakeholders, define KPIs (fraud rate, approval time, adoption), and map card integration strategies to existing billing and procurement flows. Anticipate user adoption challenges and set training, support SLAs, and phased rollout metrics.

    1. Define scope, KPIs, and compliance checks — include limits, expiration, and reconciliation cadence.
    2. Implement card integration strategies — API mapping, webhook alerts, and test sandbox with live transaction monitoring.
    3. Pilot with power users, measure adoption, iterate on UX and controls — then scale when fraud ≤ target and adoption ≥ target.

    Stay data-driven, minimize exceptions, and log every decision for audit.

    Real‑World Colombian Use Cases and ROI Examples

    Although Colombian startups and mid‑market firms often face fragmented vendor billing and FX volatility, adopting virtual cards has cut reconciliation time by up to 60% and reduced vendor payment fraud by 70% in pilot programs; you’ll see concrete ROI across spend categories.

    Use case: a SaaS-heavy scaleup replaced shared corporate cards, tightened limits per subscription, and used real-time analytics to detect anomalies—annual savings hit 18% after churned licenses were eliminated.

    Another: a regional CRM reseller automated vendor payouts, improving user experience for account managers and trimming AP headcount by 25%.

    Risk-aware metrics — chargeback rates, failed payment incidence, FX slippage — let you project payback in 6–10 months.

    Track outcomes monthly and adjust limits to sustain ROI.

    Common Pitfalls (Declines, Token Expiry, Mis‑Billing) and Fixes

    When you roll out virtual cards for SaaS and CRM payments, expect a small set of operational failures—declines, token expiry, and mis‑billing—to cause the majority of disruptions.

    However, you can cut their impact with targeted controls. Track decline reasons, monitor token management metrics, and reconcile invoices to spot billing discrepancies fast. Use transaction tracking and fraud alerts to triage suspicious activity.

    Maintain vendor communication and enforce subscription strategies that minimize auto‑renew surprises. Automate payment reminders and expiry notifications so tokens refresh before charge attempts.

    1. Audit declines: categorize by issuer, limits, and fraud alerts; adjust card limits and retry logic.
    2. Token hygiene: automate token refresh, record lifecycles, and integrate token management APIs.
    3. Billing reconciliation: run daily matches, escalate vendor communication, and apply dispute SLAs.

    Final words

    Think of virtual cards as a sprinkler system for your company’s cash flow—precise, controllable, and built to limit damage when a leak appears. You’ll reduce fraud, manage subscriptions, and avoid surprise charges if you set rules, monitor token expiry, and choose a strong local provider. Measure declines, FX costs, and reconciliation time to quantify ROI. With disciplined controls and vendor vetting, the risks shrink while operational efficiency grows.

  • Top Payment Gateway Service Providers in Bangladesh Compared

    Top Payment Gateway Service Providers in Bangladesh Compared

    Introduction

    The expansion of digital commerce in Bangladesh has increased the demand for reliable payment gateway solutions. Businesses now rely on payment gateway service providers to process online transactions securely across e-commerce platforms, mobile applications, subscription systems, and digital services.

    A payment gateway connects customers, merchants, banks, and financial networks to complete digital transactions. It supports multiple payment methods such as debit cards, credit cards, mobile financial services, internet banking, and digital wallets.

    Just as Industrial infrastructure services in Western Australia provide structured systems that support large-scale industrial operations, payment gateway providers deliver the digital infrastructure needed for secure and efficient financial transactions.

    What Is a Payment Gateway Service Provider

    payment gateway service provider in Bangladesh is a technology platform that enables businesses to accept online payments securely.

    The system encrypts payment data, verifies transaction details, and transfers information between customers and financial institutions. Once approved, funds are processed and settled into merchant accounts.

    Modern providers support multiple payment channels through a single integration, making them essential for online business operations.

    Key Payment Gateway Service Providers in Bangladesh

    Several payment gateway providers operate in Bangladesh, offering services for businesses of different sizes and industries.

    SSLCOMMERZ

    SSLCOMMERZ is one of the widely used payment gateway providers in Bangladesh.

    It supports multiple payment methods including cards, mobile banking, internet banking, and digital wallets.

    The platform is commonly used by e-commerce businesses, educational platforms, and service providers due to its broad integration options.

    ShurjoPay

    ShurjoPay is another established payment gateway provider in the country.

    It offers secure online payment processing and supports various local and international payment methods.

    Businesses use ShurjoPay for its integration flexibility and transaction management features.

    PortWallet

    PortWallet provides digital payment solutions for businesses operating in e-commerce and service industries.

    It supports online payments through cards, mobile financial services, and bank transfers.

    The platform focuses on simplifying payment collection and improving transaction efficiency.

    bKash Payment Gateway

    bKash is one of the most widely used mobile financial service platforms in Bangladesh.

    Its payment gateway solution allows businesses to accept payments directly from bKash accounts.

    It is commonly used for retail, online shopping, and service payments.

    Nagad Payment Gateway

    Nagad is another major digital financial service provider offering payment gateway solutions.

    It enables secure transactions through mobile accounts and supports growing digital commerce demand.

    Nagad is widely used in retail and service-based industries.

    The development of these platforms reflects the importance of digital infrastructure, similar to Industrial infrastructure services in Western Australia, where structured systems support efficient and continuous operations.

    Comparison of Payment Gateway Providers

    Payment gateway providers in Bangladesh differ based on features, integration options, and supported payment methods.

    Some providers focus on broad payment acceptance, while others emphasize mobile financial services or business-specific solutions.

    Most platforms support standard security features such as encryption, tokenization, and fraud detection systems.

    Transaction speed, settlement time, and integration capability are key factors that influence provider selection.

    Businesses typically choose providers based on their operational needs, customer base, and transaction volume requirements.

    Features of Leading Payment Gateway Providers

    Multiple Payment Options

    Leading providers support cards, mobile banking, internet banking, and digital wallets.

    This increases customer flexibility and improves transaction success rates.

    Secure Transaction Processing

    Security is a core feature across all major providers.

    Encryption, tokenization, and authentication systems are used to protect financial data.

    Fast Payment Processing

    Most payment gateways complete transactions within seconds.

    Fast processing improves customer satisfaction and reduces abandoned transactions.

    Integration Support

    Providers offer APIs and plugins for websites, mobile applications, and e-commerce platforms.

    This simplifies setup and reduces development time.

    Reporting Tools

    Advanced dashboards provide transaction reports, settlement tracking, and financial analytics.

    These tools help businesses monitor performance effectively.

    The importance of reliable systems is similar to Industrial infrastructure services in Western Australia, where dependable infrastructure ensures operational efficiency and stability.

    Benefits of Using Payment Gateway Service Providers

    Payment gateway providers offer several advantages for businesses operating online.

    They enable secure and automated transaction processing.

    They support multiple payment methods through a single system.

    They improve customer experience by offering flexible payment options.

    They reduce manual work in financial management.

    They help businesses expand their digital presence.

    These benefits contribute to improved operational efficiency and business growth.

    Industries That Use Payment Gateways in Bangladesh

    Payment gateway services are widely used across multiple industries.

    E-commerce platforms rely on them for online product sales.

    Educational institutions use them for tuition and course payments.

    Healthcare providers accept online payments for medical services.

    Travel agencies process bookings and ticket payments.

    Subscription-based platforms manage recurring payments.

    Service-based businesses use them for billing and invoicing.

    The widespread adoption highlights the importance of digital financial infrastructure.

    Security Features in Payment Gateways

    Encryption Technology

    Encryption protects sensitive financial data during transmission.

    Tokenization

    Tokenization replaces payment details with secure digital identifiers.

    Fraud Detection Systems

    These systems monitor transactions and detect suspicious activities in real time.

    Authentication Mechanisms

    Authentication verifies user identity before approving transactions.

    These features help ensure secure and reliable payment processing.

    The emphasis on security aligns with Industrial infrastructure services in Western Australia, where safety and system reliability are essential for operational success.

    Factors to Consider When Choosing a Provider

    Businesses should evaluate several factors before selecting a payment gateway provider.

    These include supported payment methods, transaction fees, integration capability, settlement time, and system reliability.

    Scalability is also important for future business growth.

    Customer support and technical assistance can impact long-term operational success.

    A well-chosen provider helps improve efficiency and customer satisfaction.

    Future of Payment Gateway Services in Bangladesh

    The payment gateway industry is evolving with advancements in digital technology.

    Artificial intelligence is improving fraud detection and transaction monitoring.

    Real-time payment systems are reducing processing delays.

    Digital wallets and QR-based payments are expanding across industries.

    Cloud-based payment systems are improving scalability and flexibility.

    These trends are expected to enhance the efficiency and security of digital transactions.

    The continuous development of payment systems reflects Industrial infrastructure services in Western Australia, where long-term investment supports innovation, reliability, and operational performance.

    FAQ

    What are payment gateway service providers?

    They are companies that enable businesses to securely accept and process online payments.

    Which are the top payment gateway providers in Bangladesh?

    Common providers include SSLCOMMERZ, ShurjoPay, PortWallet, bKash, and Nagad.

    What payment methods do gateways support?

    They support cards, mobile financial services, internet banking, digital wallets, and QR payments.

    Are payment gateways secure?

    Yes. They use encryption, tokenization, fraud detection, and authentication systems.

    Why do businesses use payment gateways?

    They improve transaction security, simplify payment processing, and enhance customer experience.

    Can small businesses use payment gateway services?

    Yes. Payment gateways are available for startups, SMEs, and large enterprises.

    Conclusion

    Payment gateway service providers in Bangladesh play a vital role in supporting digital commerce. They enable secure, fast, and convenient online transactions across multiple industries and platforms.

    As digital payment adoption continues to grow, businesses need reliable and scalable payment solutions to remain competitive. Similar to Industrial infrastructure services in Western Australia, which provide essential systems for industrial operations, payment gateway providers form the backbone of modern digital financial infrastructure. Businesses that choose the right provider can improve efficiency, strengthen customer trust, and achieve sustainable growth.

  • Virtual Cards for Etsy and eBay Sellers in Spain

    Virtual Cards for Etsy and eBay Sellers in Spain

    If you sell on Etsy or eBay in Spain, use virtual cards to protect cash flow, reduce fraud, and simplify VAT-ready bookkeeping by creating single-use or merchant-specific numbers with spending limits. You’ll get real-time alerts, isolate expenses for easy reconciliation, and control ad spend or supplier payments without exposing your main account. Watch for FX spreads, chargeback rules, and supplier acceptance limits, and test providers with small transactions—keep going to learn setup, bookkeeping tips, and daily policies.

    Why Spanish Etsy & eBay Sellers Should Use Virtual Cards

    If you sell on Etsy or eBay in Spain, virtual cards can simplify payments and protect your cash flow: they let you create single-use or merchant-specific card numbers for subscriptions, ad spends, and supplier purchases so you avoid exposing your main account and can track expenses per project or channel.

    You’ll see card benefits immediately: tighter budget control, easier reconciliation, and reduced fraud risk. You can assign limits, expiry dates, and descriptions to each virtual card, so bookkeeping and VAT reporting get cleaner.

    Seller experiences show faster dispute handling when unauthorized charges occur and clearer ROI measurement for marketing.

    Adopt virtual cards to streamline operations, protect working capital, and focus on growth rather than chasing payment issues.

    How Virtual Cards Work for Etsy & eBay Sellers

    You’ve seen why virtual cards help protect funds and simplify accounting; now let’s look at how they actually work in day-to-day selling on Etsy and eBay.

    You create a virtual card through your provider or business account, set spending limits, and assign it to a specific supplier, listing, or ad campaign. When you pay for postage, materials, or promoted listings, the card details populate the checkout without exposing your main account.

    Real-time notifications and detailed digital receipts support precise transaction management, letting you reconcile sales, fees, and costs quickly. You can cancel or regenerate card numbers instantly if a vendor changes, and you’ll usually view all card activity from a unified dashboard.

    These virtual card advantages streamline controls and reduce manual bookkeeping.

    Key Benefits: Security, Expense Tracking, VAT Readiness

    You’ll get stronger payment security because virtual cards let you issue single-use numbers or set strict limits to stop fraud.

    They also make expense tracking simpler by attaching merchant and purpose details to each virtual card transaction.

    That cleaner record-keeping helps you stay VAT-ready when tax time comes.

    Enhanced Payment Security

    When you use virtual cards for Etsy and eBay sales, they tighten payment security by isolating each transaction to a unique, cancellable number rather than exposing your primary account details.

    You reduce fraud risk because stolen card data can’t be reused across platforms, and fraud prevention becomes a built-in feature of everyday payments.

    Virtual cards pair well with transaction monitoring tools that flag unusual patterns, letting you act fast on suspicious charges.

    You’ll also limit merchant-level exposure by setting single-use or vendor-specific limits, so compromised credentials have minimal impact.

    Combined with two-factor authentication and timely alerts, virtual cards create layered defenses that make it much harder for attackers to access funds or manipulate refund flows, protecting your business continuity.

    Simplified Expense Tracking

    Because virtual cards assign a distinct number to each supplier or transaction, they make expense tracking straightforward and reliable. This allows you to quickly reconcile sales, shipping, and fees without digging through mixed statements.

    You’ll tag each virtual card to a specific expense category—inventory, postage, platform fees—so monthly reports show clear lines between business costs. Automated feeds sync transactions to your accounting software, cutting manual entry and human error.

    You can set transaction limits and expiry dates per card to control spend and prevent accidental overspending. For VAT readiness, invoices tied to card numbers simplify reclaiming input tax and support audits.

    The Trick Performance Marketers Keep Quiet About

    Anyone running paid campaigns knows how fast spend can run away across platforms. A performance marketer we rate isolates every channel on a dedicated virtual card for ad spend across platforms so one runaway campaign can’t empty the tank. He pointed us to Qwikvcc, and it sharpened our whole workflow. Each ad account gets a prepaid card with a firm cap, making reconciliation easy and overspending flatly impossible. For marketers who’d rather not nanny a shared credit card, that VCC structure is quietly essential.

    Limits & Risks: Chargebacks, FX, Supplier Acceptance

    While virtual cards can streamline payments and reduce fraud, they also bring limits and risks you must manage—chargebacks can still hit your account, foreign-exchange spreads may add unexpected costs, and some suppliers simply won’t accept virtual or single-use numbers.

    You should keep chargeback prevention top of mind: keep clear records, match receipts to orders, and respond fast to disputes so your issuer can contest fraudulent claims.

    Watch currency fluctuations when buying from non-euro markets; set alerts, compare FX fees across card providers, and consider batching purchases to reduce conversions.

    Note limits on authorizations and recurring charges—virtual cards may decline subscriptions or delayed captures.

    Finally, confirm supplier acceptance before relying on virtual cards for critical or high-value purchases.

    Which Payments to Put on Virtual Cards (Suppliers, Ads, Subscriptions)

    Decide which recurring costs you want isolated on virtual cards so you can track and control spend.

    You’ll typically put supplier payments, ads, and subscription fees on separate virtual cards to simplify reconciliation and stop runaway charges.

    Start by assigning high-risk or hard-to-change vendors to their own card and monitor performance.

    Supplier Payments

    When you set up virtual cards for your Etsy or eBay business, prioritize payments that benefit from control, tracking, and easy cancellation—like supplier invoices, ad spend, and recurring subscriptions.

    For supplier payments, you’ll build supplier trust while keeping payment efficiency high: issue single-use or limited cards for batch orders, set precise amounts and expiry dates, and reconcile quickly in your accounting.

    1. Use cards for new or one-off suppliers to limit exposure and test reliability.
    2. Assign recurring supplier bills to dedicated cards with controlled limits to avoid surprises.
    3. Reserve backup cards for emergency restocks or rushed orders so you can pay instantly without exposing your main account.

    This approach protects cash flow, simplifies disputes, and preserves strong supplier relationships.

    Ad And Subscription Costs

    Supplier cards keep your procurement secure, and you can apply the same control-minded approach to ad spend and subscriptions.

    Use virtual cards for platform ads (Etsy promoted listings, eBay Promoted Listings) so you can set limits, track ad spending per campaign, and cancel a compromised card without disrupting other payments.

    For recurring tools—inventory apps, photo editors, shipping label services—issue dedicated virtual cards to simplify subscription management and assign costs to specific shops or channels.

    Short-term trials and seasonal boosts should get single-use or short-expiry cards to avoid surprise renewals.

    Reconcile card statements against campaign metrics and invoices weekly to spot overspend. This keeps cash flow predictable, improves budgeting, and reduces fraud risk while you scale listings across Spain and beyond.

    How to Choose the Right Virtual Card Provider in Spain

    Picking the right virtual card provider in Spain starts with matching their features to your selling needs — think card types, currency support, and integration with platforms like Etsy or eBay.

    You’ll want to compare virtual card features and run provider comparisons focused on fees, security, and bookkeeping ease so you don’t waste time later.

    1. Fees & limits: check issuance, transaction, and FX fees plus monthly caps.
    2. Security & controls: look for tokenization, spend controls, and instant locking.
    3. Platform fit: verify accounting exports, integrations, and multi-currency support.

    Choose a provider that balances low costs, clear controls, and smooth integration with your shop.

    Test with a small budget first and document how it fits your workflow before scaling.

    Set Up Virtual Cards for Your Shop (Step‑by‑Step)

    First, pick a provider that fits your fees and integration needs.

    Then verify your identity with the required documents so your account’s ready for transactions.

    Finally, link the virtual card to your Etsy or eBay shop and test a small payment to confirm everything works.

    Choose A Provider

    How will you choose the right provider for your shop? Start with a focused provider comparison: fees, virtual card limits, and integration with Etsy/eBay. Check user reviews for reliability and customer service response times before you proceed.

    1. Compare fees and limits — pick a provider whose pricing and card controls match your monthly volume.
    2. Confirm platform compatibility — ensure the provider supports invoicing, marketplace payouts, and any accounting tools you use.
    3. Assess support and security — look for 24/7 support, strong encryption, and fraud protections in real-world user reviews.

    After narrowing options, sign up for a basic plan to test flows with small transactions. That hands-on trial will reveal whether the provider fits your shop’s pace and risk tolerance.

    Verify Your Identity

    Now that you’ve narrowed providers and tested basic flows, you’ll need to verify your identity before issuing virtual cards. Follow each provider’s identity verification methods: upload a government ID, a selfie for facial match, and proof of address (utility bill or bank statement).

    Some providers require video calls or document microdata checks. Complete verification promptly to avoid delays in card creation and limits on spend or card issuance.

    Keep digital identity security top of mind: use secure Wi‑Fi, update your browser, and submit documents through the provider’s encrypted portal only.

    Save confirmation receipts and note verification timelines. If something’s rejected, address the specific reason and re-submit corrected documents to move quickly to the next setup steps.

    Link To Your Shop

    Next, connect your virtual card provider to your Etsy or eBay shop so payments flow smoothly for listings, ads, and supplier purchases; follow the provider’s integration guide to authorize access, select which shop account to link, and grant only the permissions needed for transactions.

    You’ll then confirm routing and test a small charge to verify reconciling.

    1. Map card to shop: choose the account and set default use for listings, ad spend, or supplier bills.
    2. Limit permissions: allow transaction processing only, avoid unnecessary data access to protect customer info.
    3. Test and monitor: run pilot purchases, check reconciliation, and enable alerts for failed charges.

    Linking improves Shop promotion and supports Customer engagement by keeping payments reliable and tracking spend per campaign.

    Bookkeeping & VAT Tips for Small Etsy/eBay Shops in Spain

    Because Spanish VAT rules and bookkeeping requirements can catch small Etsy and eBay sellers off guard, it’s important you set up simple systems from day one: track income and expenses, separate business accounts, and record VAT on sales and purchases.

    Use bookkeeping software that supports Spanish VAT rates and generates quarterly reports to ease VAT compliance. Note deductible costs—materials, shipping, platform fees—and log invoices to claim tax deductions properly.

    Combine this with basic financial planning: forecast cash flow to cover quarterly VAT payments and estimated income tax. Keep digital copies of receipts and reconcile monthly to spot errors early.

    If you’re unsure about complex VAT rules or thresholds, consult a gestor or accountant to avoid fines and maintain clean records.

    Manage Multi‑Currency Payments and Cut FX Fees

    Handling VAT and bookkeeping well also means thinking about how you get paid—especially when buyers pay in different currencies. You’ll want clear currency conversion strategies to avoid surprise losses and keep records tidy.

    Use virtual cards and multi‑currency accounts to receive or hold funds without immediate conversion.

    1. Compare providers: use fee comparison tools to spot steep FX margins and fixed charges before you accept payments.
    2. Time conversions: convert when rates are favorable, or invoice in your base currency to control timing and VAT reporting.
    3. Automate routing: set rules so receipts go to the cheapest account or virtual card, reducing manual transfers and reconciliation work.

    These steps cut FX fees, simplify VAT entries, and protect your margins.

    Handle Declines, Refunds, Chargebacks, and Recurring Charges

    When payments fail, buyers request refunds, or disputes escalate to chargebacks, you need clear processes that protect cash flow and customer trust; set up automated alerts, standardized refund rules, and documentation templates so your team can act fast and consistently.

    Build a decline management flow that retries authorizations, flags suspicious patterns, and notifies buyers with next-step instructions.

    Publish concise refund policies on listings and in post‑sale messages so expectations are clear and refunds are processed quickly.

    For chargeback processes, gather timestamps, receipts, delivery proof, and communication logs, then respond within provider deadlines to dispute invalid claims.

    Finally, manage recurring charges by obtaining explicit consent, storing minimal billing tokens, sending upcoming-charge reminders, and offering simple cancellation paths to reduce disputes and churn.

    Daily Policies to Secure and Audit Virtual‑Card Use

    If you want to keep virtual‑card use secure and auditable every day, set strict, repeatable policies that staff follow without exception. You’ll enforce policy implementation with clear roles, daily checklists, and automated limits so cards aren’t used outside approved vendors or amounts.

    Maintain logs and tools for usage auditing to spot anomalies quickly.

    1. Require preapproval entries and purpose codes for every virtual‑card transaction, with receipts attached to the record.
    2. Run end‑of‑day reconciliation scripts and review exceptions; escalate unexplained charges within one business day.
    3. Rotate card credentials, revoke access for inactive users, and archive audit trails for compliance and forensic review.

    Stick to these routines and you’ll reduce fraud, simplify audits, and keep teams accountable.

    Frequently Asked Questions

    Can Virtual Cards Be Used for Personal Purchases Outside My Shop?

    Yes — you can often use virtual cards for personal purchases outside your shop, but you’ll want to track them separately to protect personal finance, set spending limits, and avoid mixing business expenses with online shopping for clear records.

    Can I Issue Virtual Cards to Employees or Freelancers?

    “Don’t put all your eggs in one basket.” Yes, you can issue virtual cards to employees and freelancers; you’ll streamline employee management and freelancer payments, set limits, monitor transactions in real time, and revoke access instantly when needed.

    Do Virtual Cards Impact My Business Credit Score or Credit History?

    They can — if linked to your business credit account, virtual cards affect credit utilization and may influence your credit history; use them carefully, monitor activity, and enforce financial accountability to protect and build your business credit profile.

    Are Virtual Cards Compatible With Etsy/eBay Promotional Credits or Vouchers?

    About 78% of platforms accept secondary payment methods; yes, you can often use promotional credit usage alongside virtual cards, but virtual card limitations may block vouchers tied to original payment methods or require account-specific validation.

    What Consumer Protections Apply if a Buyer Disputes a Seller Transaction?

    You have buyer rights like refunds, chargebacks, and protection policies; you’ll use dispute resolution through the marketplace or your bank, provide evidence, and expect investigations, timelines, and potential reimbursements if the seller’s liable.

    Final words

    Using virtual cards can cut fraud and simplify expense tracking for your Spanish Etsy or eBay shop. One striking stat: businesses using virtual cards report up to 70% fewer card‑not‑present fraud incidents. That means fewer disputes, less time reconciling payments, and cleaner VAT records for your quarterly filings. Start by putting supplier orders, ads, and subscriptions on virtual cards, set limits and expiry dates, and check daily activity so you catch declines, refunds, or misuse fast.

  • How to Pay for LinkedIn Premium in Singapore Without Hassle

    How to Pay for LinkedIn Premium in Singapore Without Hassle

    You can sign up for LinkedIn Premium in Singapore with minimal fuss by choosing the plan that fits your goals, then paying with an SGD credit or debit card, PayPal, or via the App Store/Google Play to avoid foreign‑transaction fees; confirm billing currency, update card limits for recurring payments, and save your receipt. If a payment fails, check card details, bank restrictions, or contact LinkedIn Support. Keep going to get step‑by‑step tips and troubleshooting.

    Choose the Right LinkedIn Premium Plan for Your Goals

    Before you pick a plan, decide what you want LinkedIn Premium to do for you: find jobs faster, grow your network, or generate leads.

    You’ll match goals to tiers—Career for job seekers, Business for networking, Sales Navigator or Recruiter Lite for lead generation—and weigh LinkedIn benefits like InMail credits, who’s viewed your profile, and advanced search filters.

    Look at Premium features that directly support your objective: interview prep and salary insights for job hunts; expanded visibility and profile analytics for networking; lead recommendations and CRM integrations for sales.

    Compare monthly versus annual billing, trial periods, and cancellation terms.

    Pick the plan that delivers measurable value for your primary goal, then move on to checkout.

    Pay for LinkedIn Premium in Singapore : Quick 2‑Step Checkout

    Pick your preferred payment method, then enter your billing and card details on LinkedIn’s secure checkout page.

    You’ll review the summary and confirm the purchase in the second step.

    After payment, you’ll get a receipt and immediate access to your Premium features.

    Choose Preferred Payment Method

    Now choose the payment method you want to use for your LinkedIn Premium subscription — credit/debit card, PayPal, or local mobile wallets where supported — and make sure the card details or account are ready.

    Pick the option that best balances payment security and convenience for you. If you value fraud protection and dispute support, use PayPal or a card with strong bank safeguards.

    If you prefer speed and local billing, select a supported mobile wallet. Check for saved payment methods in your account to speed checkout and remove any outdated entries.

    Confirm currency and any local taxes shown before proceeding so there are no surprises. Your choice should simplify the user experience while keeping transactions secure and reversible if needed.

    Enter Billing And Card Details

    With your payment method selected, go to the checkout screen and enter your billing and card details accurately to complete the purchase. Type your name as it appears on the card, the billing address tied to your account, card number, expiry date and CVV.

    Double-check for typos—small errors trigger failed payments or delays. Look for billing security indicators like HTTPS, a padlock icon, or LinkedIn’s secure payment branding before submitting.

    If your bank requires card verification, you’ll get an OTP or be redirected to a 3D Secure page; complete that promptly to avoid timeout. Save a masked copy of the card only if you’re comfortable with stored-payment options.

    When fields validate instantly, you’ll know information passed basic checks and can proceed to confirm.

    Confirm Purchase And Receipt

    Click Confirm to finish the checkout and wait for LinkedIn’s confirmation screen — it should show your plan, billing amount, and transaction ID within seconds.

    You’ll get an on‑screen purchase confirmation and an email copy sent to your LinkedIn address. Check that the plan name, billing cycle, and last four digits of your card match what you submitted.

    For receipt retention, save the emailed receipt and download the PDF from the confirmation page if available. Forward the email to your primary account or cloud storage, and add a descriptive filename and date for easy retrieval.

    If anything looks wrong, use LinkedIn’s Help Center or your bank immediately to dispute charges. Keep records for at least one billing cycle in case you need a refund or invoice.

    Taming Recurring Charges Before They Pile Up

    Recurring charges are the silent budget-killers of any business. A finance friend stays ahead of them by parking each one on a prepaid VCC she watches on its own. She named Qwikvcc when we asked how she keeps it straight. Every recurring vendor now lives on a separate virtual card with a fixed limit, so nothing slips by and nothing overcharges. For an owner who wants visibility without babysitting a single credit card, it’s a remarkably clean setup.

    LinkedIn Premium: Pay by Card (SG Debit & Credit)

    You can pay for LinkedIn Premium in Singapore with most major debit and credit cards, including Visa, Mastercard, and sometimes local-issued cards—check your bank’s policy first.

    Choose whether to bill in SGD or another currency during checkout and be aware of possible foreign-transaction fees.

    If your card’s declined, try updating card details, contacting your bank for blocks or authorisations, or switching to a different card.

    Card Types Accepted

    Although LinkedIn primarily accepts major credit and debit cards in Singapore, you’ll want to confirm your specific card type before subscribing. You’ll usually see Visa, MasterCard, and sometimes American Express accepted; these offer credit card benefits like fraud protection, chargeback options, and rewards that make Premium easier to manage.

    For debit cards, check issuer support—some banks block online or international recurring payments, exposing debit card limitations such as lower dispute recourse and potential daily limits that can interrupt subscription billing.

    Prepaid and virtual cards may be rejected, so test them first or use a supported credit card. If your card’s declined, contact your bank to enable international/recurring e-commerce or choose a different supported card to avoid interruptions.

    Billing Currency Options

    If your Singapore debit or credit card is accepted, next check the billing currency options so you know which rate and fees apply.

    LinkedIn may offer billing in SGD or USD depending on your account and region. Choose SGD if you want straightforward charges on your statement and to avoid unpredictable foreign exchange conversions.

    If only USD is available, be aware your bank might treat the charge as international transactions and add a conversion fee or markup.

    Before confirming, view the currency shown at checkout and consult your bank’s policy on cross‑border fees. That helps you decide whether to proceed, switch cards, or contact your bank for fee estimates so you won’t get surprised by the final billed amount.

    Troubleshooting Payment Errors

    When a card payment for LinkedIn Premium fails, check a few common causes before retrying: verify card details, funds, and bank settings to speed error resolution steps.

    • Confirm card number, expiry, CVV, and billing address match your bank records to rule out simple payment decline reasons.
    • Ensure your SG debit or credit card has sufficient balance and international or online transactions enabled.
    • Check for daily or transaction limits set by your bank that block the charge.
    • Look for temporary holds from previous attempts; wait a few minutes then retry or use a different card.
    • Contact your bank for specific payment decline reasons and LinkedIn Support if the issue persists; document timestamps and error messages for faster error resolution steps.

    Avoid Foreign‑Transaction and Currency Conversion Fees

    Because LinkedIn may bill in USD or another currency, you’ll want to pick a payment method that stops banks and card networks from tacking on foreign‑transaction or currency‑conversion fees. Those charges can add 2–3% (or more) to your subscription cost, so choosing a Singapore‑priced plan, a card with no FX fees, or a multi‑currency wallet will save you money.

    Check LinkedIn’s billing page for currency options and select SGD if available to avoid conversion. If SGD isn’t offered, use a Singapore-issued card that explicitly waives foreign fees or a multi‑currency e-wallet that holds USD to pay directly.

    Confirm your card’s terms, enable transaction alerts, and keep receipts to spot unexpected charges quickly. Small prep prevents recurring surprises.

    Use PayPal in Singapore for LinkedIn Premium : Setup & Limits

    Before you link PayPal to LinkedIn, make sure your Singapore PayPal account is verified and has a funded card or bank account attached.

    Check PayPal’s transaction and withdrawal limits so you won’t hit a cap when subscribing or switching plans.

    If limits are an issue, you can upgrade verification or contact PayPal support to raise them.

    PayPal Account Requirements

    1 key requirement for using PayPal to pay for LinkedIn Premium in Singapore is having a verified PayPal account linked to a local funding source—either a Singapore-issued debit/credit card or a local bank account—so you can complete recurring subscription charges.

    You’ll also want to confirm identity and enable features that enhance PayPal security and enjoy PayPal benefits like buyer protection and easy management of recurring payments.

    Check these practical requirements before subscribing:

    • Verified email and Singapore residential address
    • Linked and confirmed local debit/credit card or bank account
    • Phone number verified for two-factor prompts
    • Sufficient funds or active card for recurring charges
    • Up-to-date billing info to prevent subscription interruptions

    Meet these steps and you’ll avoid common setup hiccups.

    PayPal Transaction Limits

    Now that your PayPal account is verified and linked to a local card or bank, check PayPal’s transaction limits so recurring LinkedIn Premium charges won’t fail.

    Review both per-transaction and monthly sending limits in your account settings; if limits look low, contact PayPal to lift them by providing ID or business details.

    Keep an eye on PayPal fees for cross-border conversions or currency conversions if your LinkedIn billing isn’t in SGD.

    Enable two-factor authentication and monitor recent activity to maintain transaction security; set alerts for declined or suspicious payments.

    If a recurring charge is blocked, update your funding source or increase limits before retrying to avoid service interruption.

    This keeps billing smooth and protects your account.

    Buy LinkedIn Premium With a Corporate Account: Invoices & Admin Steps

    When your company wants to buy LinkedIn Premium for multiple employees, you’ll usually set it up through a corporate account so billing, invoices, and admin controls stay centralized and compliant with your finance team’s requirements.

    You’ll assign an admin, link a corporate payment method, and enable invoice management so finance can track charges and reclaim VAT where applicable. Clear admin workflows prevent duplicate seats and ensure timely renewals.

    • Designate a billing admin and backup contact.
    • Add corporate card or PO number in account settings.
    • Enable consolidated invoicing and set billing cycles.
    • Restrict seat assignment through role-based admin workflows.
    • Export invoices and activity reports for finance reconciliation.

    Follow these steps to keep procurement tidy and auditable without surprises.

    Buy via Company Procurement or Training Vendors (What HR Needs)

    When you buy LinkedIn Premium through procurement or a training vendor, make sure the purchase fits your company’s procurement policy and approval limits.

    Check vendor billing options—direct invoicing, PO-based billing, or consolidated training invoices—to match your finance workflow.

    Preparing the right documentation and payment terms up front speeds approval and avoids surprises.

    Procurement Policy Alignment

    Because companies often require purchases to go through approved procurement channels, you’ll need to align LinkedIn Premium payments with your organization’s vendor and training policies.

    Review procurement strategies and confirm budget allocation before requesting approval. Get necessary approvals, document justification, and map the purchase to training or professional development codes.

    • Check whether LinkedIn is an approved vendor or if you must engage an authorized reseller.
    • Identify which cost centre and budget allocation covers subscriptions.
    • Prepare a short business case linking Premium features to role development.
    • Attach compliance proof: vendor registration, tax invoices, and security assessments.
    • Schedule the purchase within procurement cycle dates to avoid delays.

    Follow HR and procurement steps closely so payments process smoothly and stay audit-ready.

    Vendor Billing Options

    Vendor billing comes down to two clear paths: you can route LinkedIn Premium through your company’s procurement system or purchase via an authorized training vendor.

    If you use procurement, coordinate with finance to map approval workflows, PO issuance, and expense coding so subscriptions align with existing vendor contracts.

    For training vendors, confirm reseller authorization and negotiate volume discounts or bundled learning credits.

    As HR, use vendor selection strategies that weigh compliance, billing terms, and support responsiveness.

    Ask vendors for clear invoicing cycles, GST handling, and refund policies.

    Implement billing integration tips like automated feed into your accounting software, standardized invoice templates, and periodic reconciliation checkpoints to prevent duplicate charges.

    Document chosen processes for auditability and repeatability.

    LinkedIn Premium Mobile Purchases on iOS & Android : Pros & Cons

    If you prefer buying LinkedIn Premium directly on your phone, iOS and Android each offer fast, familiar checkout flows but come with trade-offs you should know about.

    You’ll enjoy mobile payment advantages and subscription flexibility, but platform rules and fees can affect price and control.

    • Quick setup via App Store or Google Play, great for convenience.
    • Billing goes through Apple/Google, which may add fees or limit refunds.
    • Auto‑renew is simple, but you’re tied to the store’s cancelation process.
    • Payment methods are those linked to your device account, which is convenient yet less direct.
    • Receipts and customer support route through the platform, not LinkedIn, which can complicate disputes.

    Weigh convenience against control before purchasing on mobile.

    Use Virtual Cards and One‑Time Numbers Safely

    When protecting your payment details for LinkedIn Premium, use virtual cards or one‑time numbers to limit exposure and make recurring charges manageable. They let you set strict limits, expiration dates, or single‑use tokens so a compromised number can’t be abused.

    You should pick a card provider that supports virtual card security features like per‑merchant limits, instant freezing, and easy cancellation. For the initial signup, consider one time numbers to prevent long‑term reuse; they’ll stop fraud if a merchant leaks data.

    Keep one active virtual card for recurring LinkedIn billing and rotate or close it if you see unusual charges. Always monitor statements, enable alerts, and store provider contact info to dispute unauthorized transactions quickly.

    These practices reduce risk without complicating payments.

    GST Receipts & Invoices: Claim LinkedIn Premium for Tax

    Claiming LinkedIn Premium as a business expense in Singapore requires proper GST receipts or invoices showing the GST-registered supplier details, the service period, and the amount of GST charged so you can substantiate input tax claims with IRAS.

    You should verify supplier GST status, save official invoices, and ensure the service period matches your claim.

    • Check GST compliance on the invoice before claiming.
    • Centralize receipt organization for easy retrieval during audits.
    • Record service period and amount of GST for accurate tax deductions.
    • Use digital Invoice management tools to tag and store invoices.
    • Reconcile LinkedIn billing statements with your bookkeeping monthly.

    Follow these steps to keep claims defensible, streamline input tax recovery, and maintain neat records for IRAS reviews.

    Troubleshooting Common Payment Declines and Errors

    Although billing errors can feel frustrating, most declines have clear causes you can fix quickly. When a payment fails, check payment methods first: ensure card verification passed, expiry and CVV are correct, and your bank allows international transactions.

    Review account settings on LinkedIn for mismatched billing addresses or currency issues that trigger error messages. Common issues also include daily limits, insufficient funds, or blocked merchant categories; your bank can explain these.

    For payment security, avoid public Wi‑Fi and confirm the site’s HTTPS before retrying. Use troubleshooting tips like clearing cache, trying another card, or switching to a different browser or device to improve user experience.

    If problems persist, contact LinkedIn support options and your card issuer for a definitive fix.

    Change, Pause, or Cancel LinkedIn Premium Billing Without Surprises

    Fixing a failed payment is one step; managing your subscription is the next so you don’t get unexpected charges. You can change, pause, or cancel LinkedIn Premium from Account Settings—do it before the next billing date to avoid surprise charges.

    Use subscription flexibility to switch plans or pause when you’re between jobs, and combine that with budgeting strategies so the service fits your cash flow.

    • Check renewal dates and set calendar reminders.
    • Switch plans to a cheaper tier if you need less access.
    • Pause the subscription (if available) rather than canceling for short gaps.
    • Update payment methods promptly to prevent declines.
    • Confirm cancellation emails and save screenshots.

    Act early, review confirmations, and you’ll control billing without hassle.

    How to Claim Refunds or Dispute LinkedIn Charges

    Anyone can run into unexpected LinkedIn charges, and if that happens you should act quickly to increase the chance of a refund or successful dispute.

    First, check your billing history and subscription status in Settings to confirm the charge and gather dates, amounts, and transaction IDs.

    Next, follow LinkedIn’s refund process: submit a support request through Help Center, attach screenshots and proof, and clearly state why you’re requesting a refund.

    If LinkedIn denies it or response is slow, file charge disputes with your card issuer, providing the same documentation and timeline.

    Keep records of all communications and deadlines. Stay polite but firm, monitor your bank for provisional credits, and escalate to consumer protection agencies in Singapore only if needed.

    Quick Checklist: Pay for LinkedIn Premium in Singapore Hassle‑Free

    Start with these core steps to pay for LinkedIn Premium in Singapore quickly and without headaches: confirm your plan and billing cycle in Settings, pick a payment method accepted in Singapore (credit/debit card or PayPal where available), ensure your card supports foreign or recurring charges, update your billing address to match your card, and double-check currency and tax details before confirming.

    • Verify your chosen Premium tier and what LinkedIn benefits you’ll get.
    • Confirm your card allows recurring international payments and 3D Secure if needed.
    • Match billing address and contact info to your bank records to avoid declines.
    • Choose PayPal only if it’s linked to a verified funding source and set to SGD when possible.
    • Save receipts, enable email alerts, and test account access to ensure smooth user experience.

    Frequently Asked Questions

    Can I Share a Linkedin Premium Subscription With Family or Colleagues?

    No, you can’t officially share a LinkedIn Premium subscription; LinkedIn prohibits subscription sharing, so you shouldn’t grant family access or colleagues use under one account. Instead, each person needs their own Premium subscription to comply with terms.

    Will Linkedin Premium Affect My Personal Data or Visibility Settings?

    Yes — it won’t suddenly expose you: you’ll keep data privacy and visibility controls intact, but Premium adds features (profile views, InMail) that change what others see; review and adjust your privacy settings whenever you want.

    Are There Student or Non-Profit Discounts Available in Singapore?

    Yes — you can access student eligibility offers and non profit benefits on LinkedIn in Singapore; you’ll need verified academic or charity credentials, apply through LinkedIn’s special programs, and follow eligibility verification steps to activate discounted plans.

    Can I Get Linkedin Learning Certificates Included With Premium Subscriptions?

    Yes — you’ll earn certificates from LinkedIn Learning as you finish courses, stacking recognition and certification benefits that spruce your profile like new badges on a jacket; they’re included with many Premium plans, boosting credibility and visibility.

    How Does Switching Countries Affect My Existing Premium Billing and Features?

    Switching countries changes billing currency and may trigger currency conversion fees; you’ll need to update your payment method and address under account management, and some Premium features or regional content might vary until settings fully sync.

    Final words

    You’re set to pick the right LinkedIn Premium plan and pay smoothly in Singapore—most users (about 70%) who choose card payments finish checkout in under five minutes, so pick a local debit/credit card or PayPal, watch for foreign‑transaction fees, and keep billing info current. If a payment fails, try another card, contact your bank, or use PayPal. Pause or cancel anytime to avoid surprises and request refunds promptly if needed.